Shadow AI: Govern It by Enabling It, Not Banning It
Over 80% of workers use unapproved AI tools, and IBM found shadow AI incidents at 43% of breached organizations in 2026. Govern shadow AI by enabling it: make the sanctioned path easier than the workaround.
Shadow AI is already in your business, whether or not you approved it. More than 80% of workers use AI tools their employer never sanctioned, and only about a third of organizations can even detect it. The reflex is to ban it. The evidence says banning makes it worse. The better move is to govern shadow AI by enabling it: give people a safe, sanctioned path that is easier than the one they are already taking.
I am Amelia Gagne, CEO of Kief Studio. I want to make the case for enablement over prohibition, because the fear framing around shadow AI leads managers straight to the one response that reliably backfires. The goal is to make the safe way the easy way, so good people doing good work do not have to route around you to use AI.
The short version: shadow AI is common, mostly well meant, and costly when it goes wrong. IBM's 2026 research found shadow AI incidents at 43% of breached organizations, up from 20% a year earlier. Bans push the use out of sight. A sanctioned path that is easier than the workaround brings it back into view.
Find out which AI tools people already use, without blame.
Approve a small set of tools on business accounts, not personal ones.
Write a one-page policy: what data may go in, what may not, who to ask.
Give people a fast way to request a new tool.
Review usage every quarter and adjust the lane.
What shadow AI actually is, by the numbers
Shadow AI is the use of AI tools and accounts outside your organization's visibility or policy. It is common, and it usually comes from people trying to do their jobs faster. UpGuard's research found more than 80% of workers use unapproved AI tools, and nearly half do it through personal accounts the company never sees. Cybersecurity Dive's November 2025 coverage of the UpGuard report adds that about half of workers use unapproved AI tools regularly and fewer than 20% use only the tools their company approved.
The exposure is real because of where the data goes. IBM's 2025 Cost of a Data Breach report found that breaches involving shadow AI carried a cost premium, with organizations that had high levels of shadow AI paying about $670,000 more than those with low levels or none, and that one in five organizations had already had a breach linked to unsanctioned AI. This is the practical reason what AI can and cannot do with your business data deserves a real answer, not a shrug. In IBM's 2026 report, security incidents involving shadow AI more than doubled to 43% from 20%, and those breaches averaged USD 5.39 million, up from USD 4.63 million the year before.
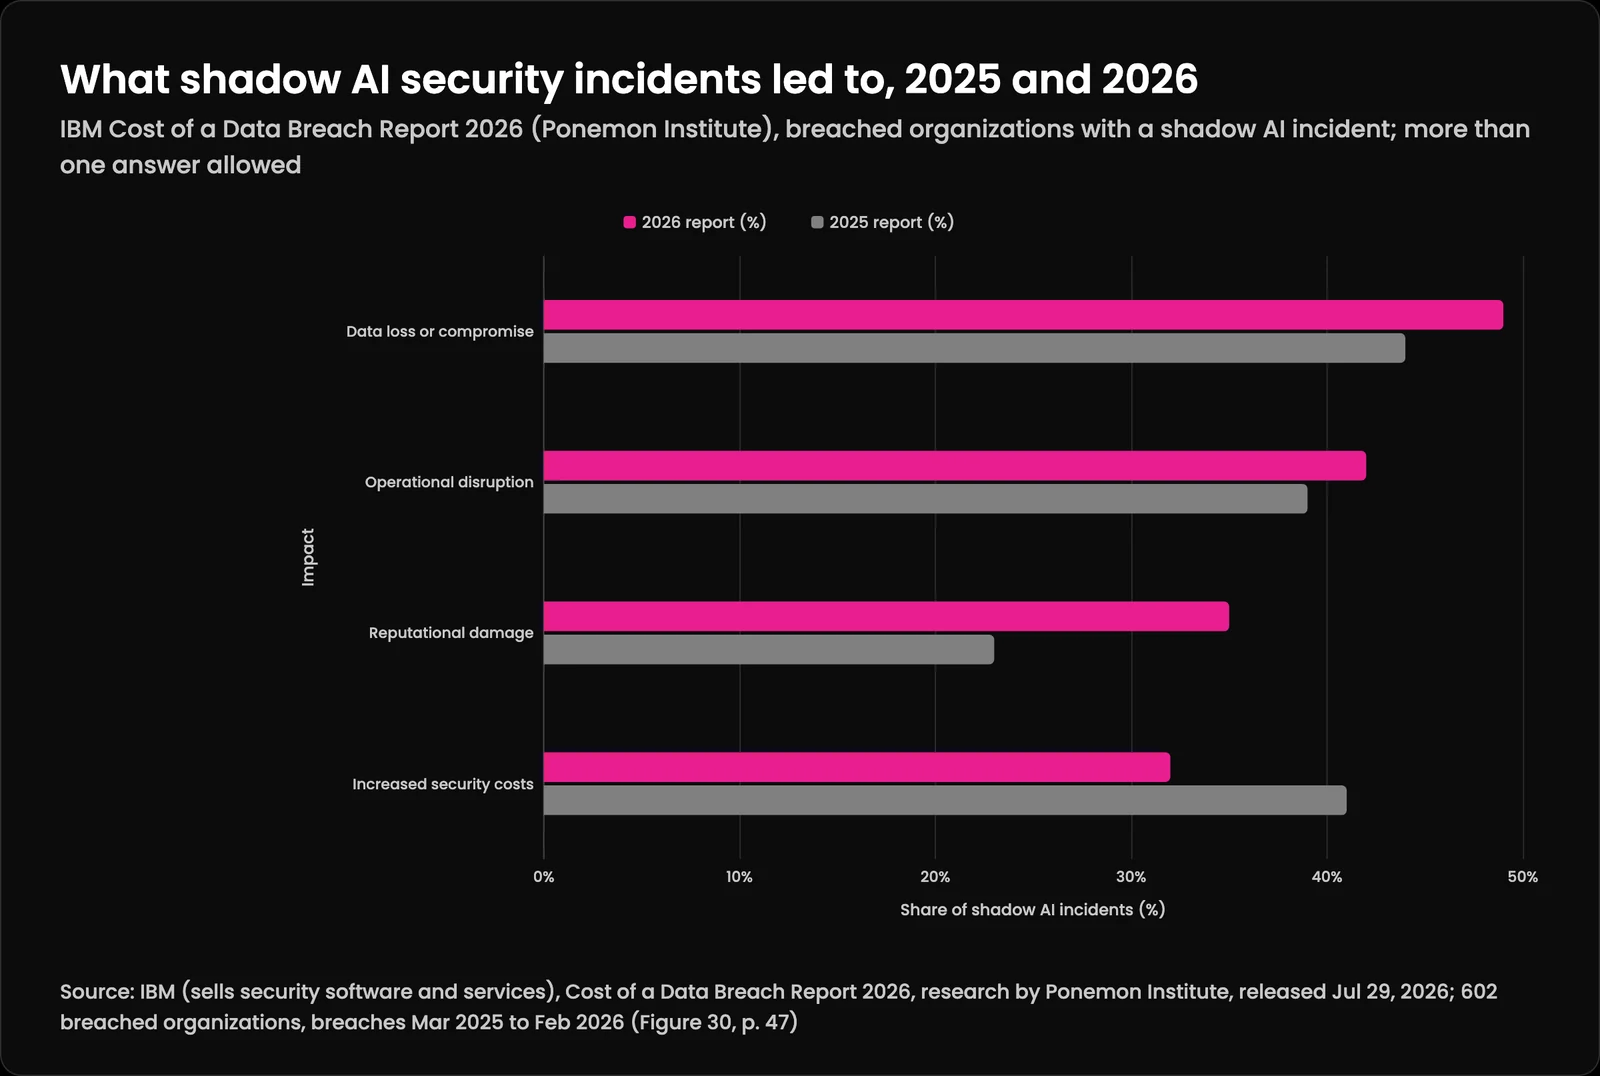
Shadow AI incidents caused data loss more often in IBM's 2026 report than in 2025, and reputational damage rose from 23% to 35%.
What shadow AI security incidents led to, 2025 and 2026 (IBM (sells security software and services), Cost of a Data Breach Report 2026, research by Ponemon Institute, released Jul 29, 2026; 602 breached organizations, breaches Mar 2025 to Feb 2026 (Figure 30, p. 47))
Impact
2026 report (%)
2025 report (%)
Data loss or compromise
49%
44%
Operational disruption
42%
39%
Reputational damage
35%
23%
Increased security costs
32%
41%
Shadow AI is not malicious. It is faint, scattered, and out of sight: people doing their jobs faster than policy has caught up.
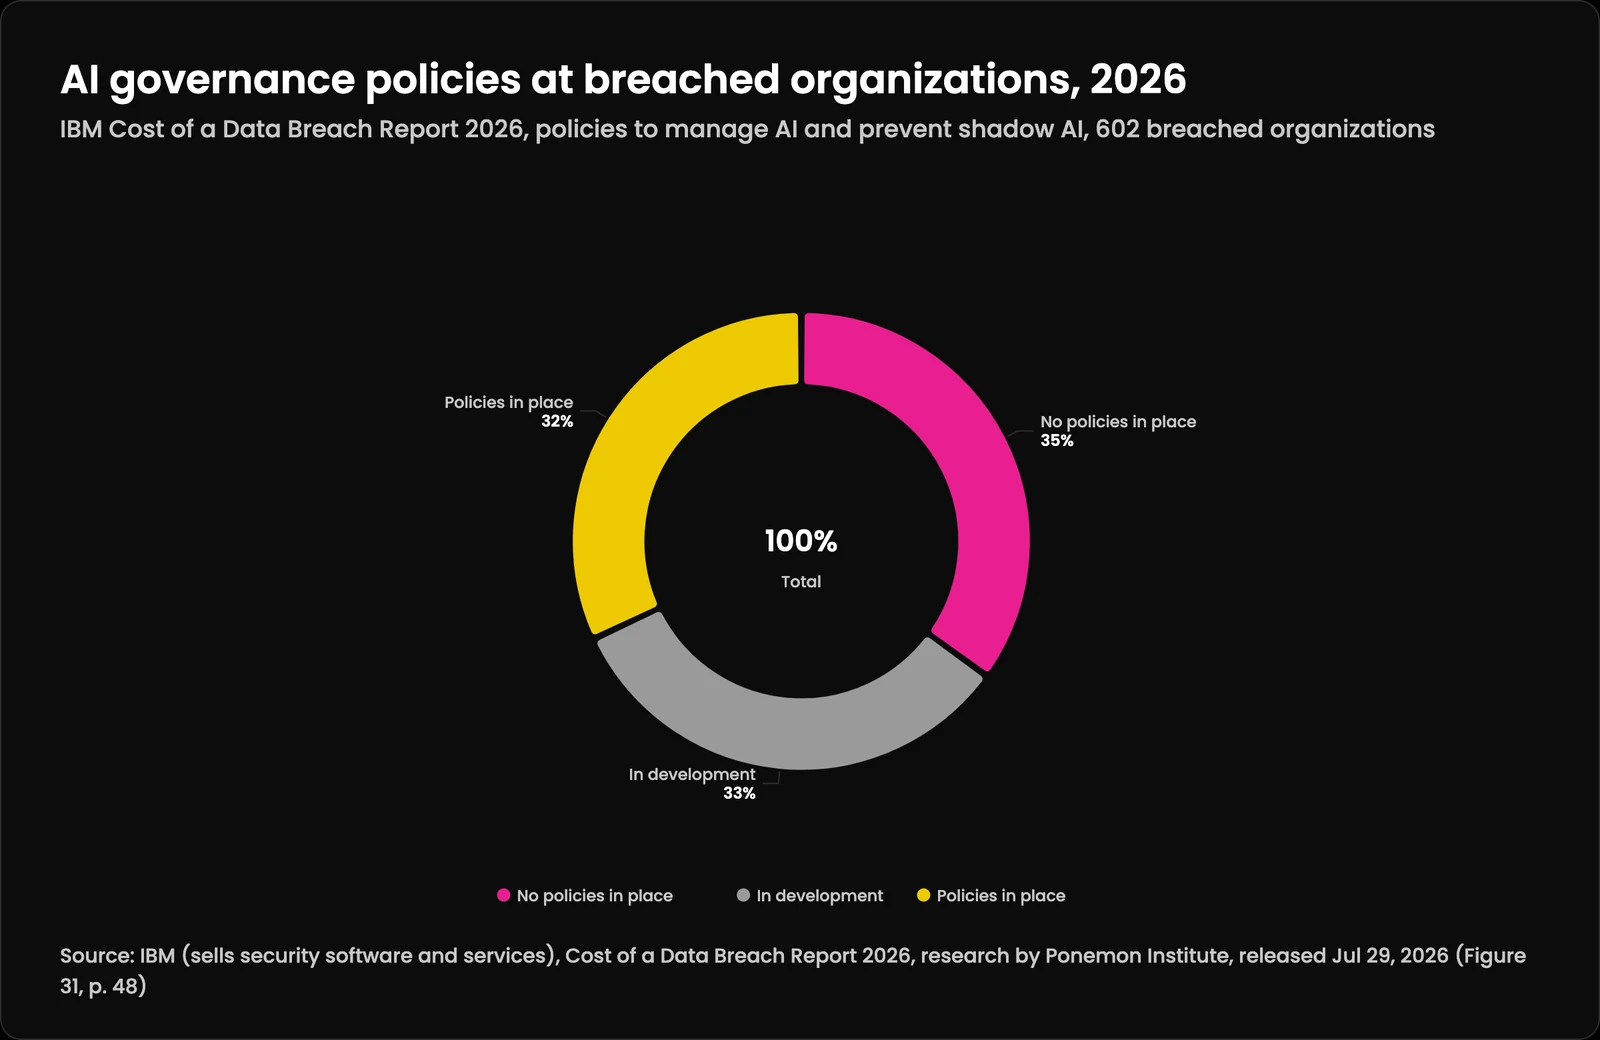
Part of the gap is that only 37% of organizations have any policy to manage or even detect shadow AI, a figure from IBM's 2025 report. The honest read is that the workforce adopted a powerful tool faster than leadership built a lane for it. That is a governance gap rather than a sign of reckless employees, and you close it the way you close any culture gap, which is the same lesson as building a security culture when everyone thinks it is IT's job. IBM's 2026 report puts that share at 32% of breached organizations, with 35% having no AI governance policy and 33% still developing one.
Two in three breached organizations in IBM's 2026 report had no AI governance policy in place, though a third were writing one.
AI governance policies at breached organizations, 2026 (IBM (sells security software and services), Cost of a Data Breach Report 2026, research by Ponemon Institute, released Jul 29, 2026 (Figure 31, p. 48))
Policy status
Breached organizations (%)
Policies in place
32%
No policies in place
35%
In development
33%
Govern by making the sanctioned path the easy one: brighter and smoother than the workaround beside it.
Govern by enabling, not by forbidding
Enablement is concrete, and it starts before any tool decision. Give people sanctioned options good enough that the unsanctioned ones lose their appeal. Make the approved path the path of least resistance, with clear, short guidance on what data may and may not go into which tools.
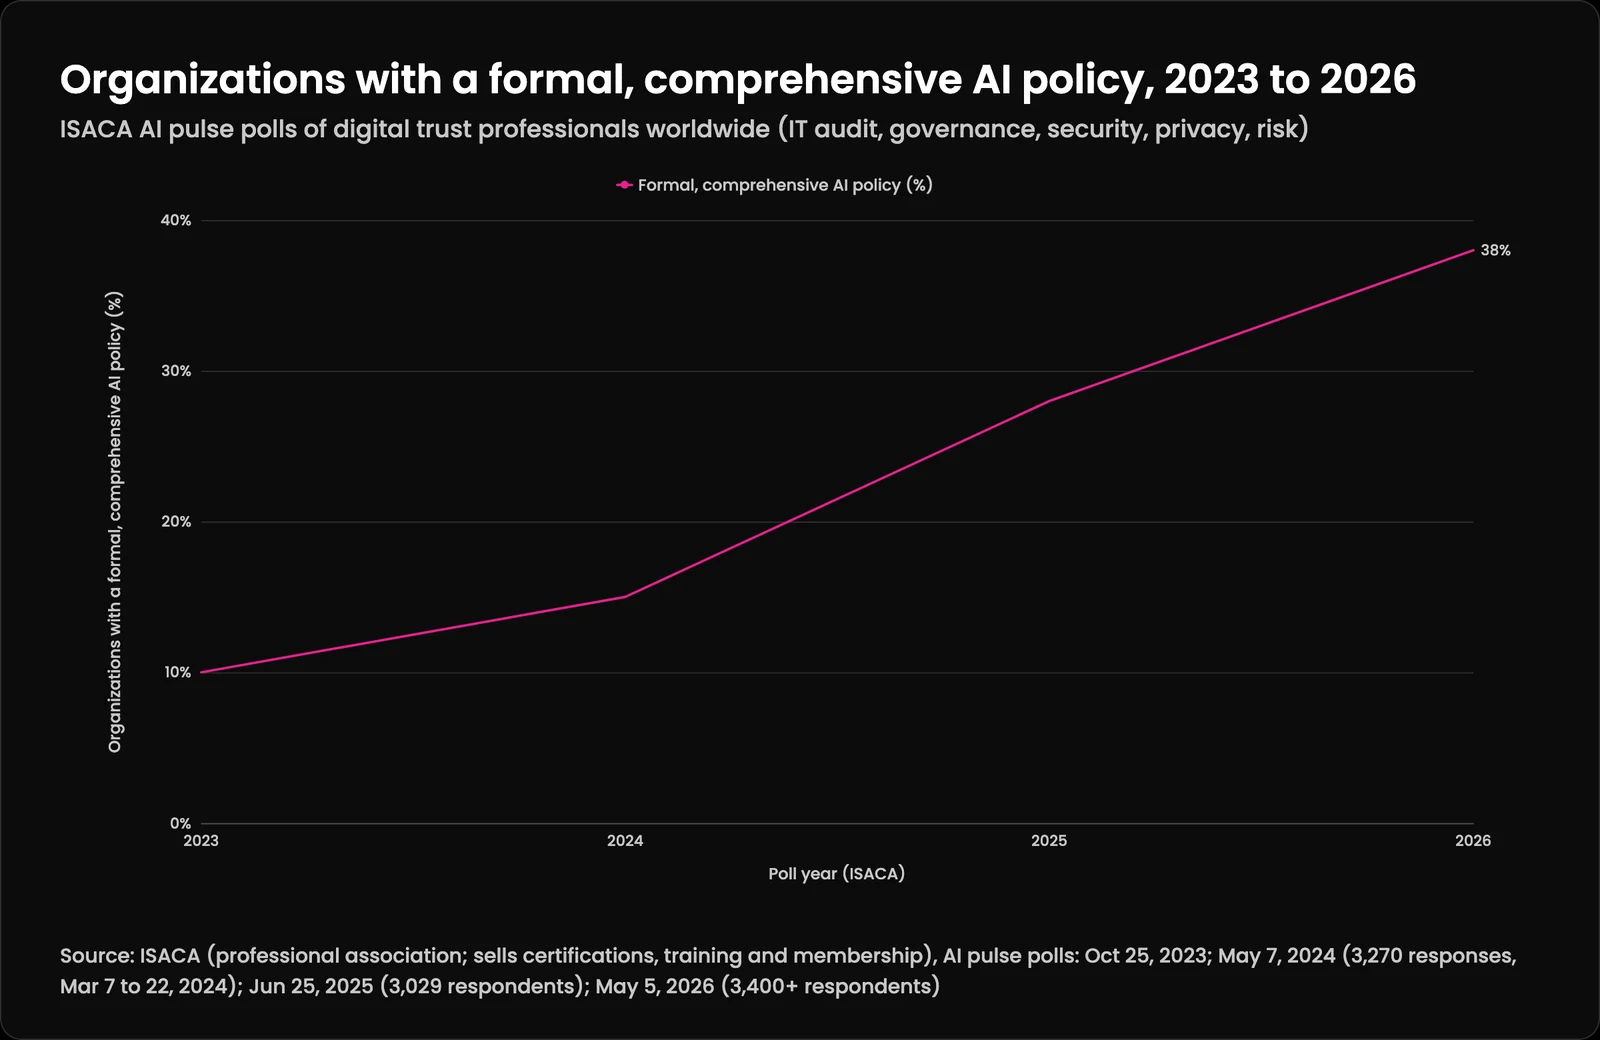
Write the policy before you need it, in plain language, the way I lay out in how to build an AI policy for your team before you need one. A good policy is permissive about value and strict about data: here is what you can do freely, here is the small set of things you cannot, here is where to go when you are unsure. Pair it with the kind of visibility I describe in how to audit what AI is actually doing in your business, so governance is based on what is real rather than what you hope. And choose tools on their merits, not their hype, which is the whole point of evaluating AI tools without getting sold. In ISACA's yearly AI polls, the share of organizations with a formal, comprehensive AI policy rose from 10% in 2023 to 38% in 2026.
Formal AI policies nearly quadrupled in ISACA's polls from 2023 to 2026, yet most organizations still work without one.
Organizations with a formal, comprehensive AI policy, 2023 to 2026 (ISACA (professional association; sells certifications, training and membership), AI pulse polls: Oct 25, 2023; May 7, 2024 (3,270 responses, Mar 7 to 22, 2024); Jun 25, 2025 (3,029 respondents); May 5, 2026 (3,400+ respondents))
Poll year
Formal, comprehensive AI policy (%)
2023
10%
2024
15%
2025
28%
2026
38%
Most shadow AI risk is a data question. Gather the scattered data into one governed stream and sanctioning AI gets simple.
Enablement is a data-governance problem in disguise
Most shadow AI risk is really a data-governance question with an AI label on it. The danger is sensitive data leaving your control without anyone deciding it should. If your data is already organized and governed, sanctioning AI is straightforward. If it lives in four SaaS tools and a group chat, every new tool multiplies the exposure. That is why I treat this as a starting point for data governance rather than a bolt-on.
The studios and teams that handle this well made the sanctioned path obvious, governed the data underneath, and trusted their people with a clear lane, rather than relying on the strictest bans. That is the same advice I give in what I tell every CEO who asks me about AI: your team will use these tools. Your only real choice is whether they use them in the light or in the dark, and building the lane is how you keep them in the light.
What does shadow AI do inside a business?
In practice, shadow AI looks ordinary. Someone pastes a difficult customer email into a personal chatbot to draft a calmer reply. A salesperson installs a browser extension that summarizes every page they open, including the CRM. A manager lets a free note-taker join a client call. An AI feature gets switched on inside a tool you already pay for, and nobody checks what it does with the data. A developer uses a coding assistant on a personal account and pastes in a config file that holds a key.
Each of those moves sends company information to a service you have no agreement with. The questions that matter are the same every time: who stores that text, for how long, whether it trains a model, and who at the vendor can read it. Brian Gagne, Kief Studio's CTO and co-founder, walks through how the answer changes by account type in whether staff can put customer data into AI tools; the short answer is that the account matters more than the brand.
Shadow AI also does real good, which is why people keep using it. In the Software AG survey, workers using their own AI tools said it saved them time and made their jobs easier, which is useful information: the tasks people quietly hand to AI are a map of where your team wants help, and a good sanctioned lane starts with those tasks.
How do you govern shadow AI without blocking it?
This is the question I hear most, and the answer is a short, repeatable process. None of it needs a big budget.
Find it without blame. Ask the team which AI tools they use and for what, and promise that the answers will not get anyone in trouble. Then check what your systems already show: single sign-on and OAuth grants in your email and file admin consoles, browser extensions on managed machines, and card statements for small AI subscriptions.
Sort the uses by data, not by tool. Drafting a social post from public facts is low risk. Pasting a client contract, a payroll file or health information is high risk. Most of your policy follows from that split.
Approve a small set of tools on business accounts. Business and enterprise plans usually come with admin controls, retention settings and contract terms that personal accounts lack. Approve one or two that cover the common jobs well.
Write a one-page policy. Say what is allowed freely, what data never goes in, which outputs need a human check, and who to ask. Qurtoo's AI acceptable use policy template is a good starting draft for a small team.
Make requests fast. If someone needs a tool you have not approved, give them a simple way to ask and an answer within days. A slow request process is how a new workaround starts.
Review every quarter. Look at what people actually use, retire what nobody needs, and add what they keep asking for.
Can you govern shadow AI for free? Mostly, yes. The survey, the admin-console review, the policy and the quarterly check cost time, not money. The frameworks below are free to read. The one place I would spend is on business accounts for the approved tools, because the contract terms are what move a tool from shadow AI to sanctioned AI.
Is there an app that blocks AI, and should you use one?
Yes. Web filters, DNS filtering, managed browser policies and secure web gateways can all block known AI sites, and many security suites now include an AI category you can switch off. They work as far as they reach. They do not reach a personal phone, a home laptop, or an AI feature built into a tool you already approved.
That is why blocking alone tends to fail. When 46% of workers in the Software AG survey said they would keep their own tools under a full ban, the block moves the work to devices you cannot see. IBM's 2026 report found the most common AI governance control, requiring IT approval for AI deployments, in place at 38% of breached organizations, down from 45% the year before. Approvals and visibility are slipping while use climbs.
Blocking has a place in a sanctioned lane. It is reasonable to block uploads of regulated data to unknown services, or to block a specific tool whose terms you have read and rejected. A narrow block like that supports the lane, as long as the lane exists first.
Is there an AI governance framework a small business can use?
There are two well-established ones, and a small business can borrow from both without adopting either in full.
The NIST AI Risk Management Framework, released January 26, 2023, is free and voluntary. It organizes the work into four functions: Govern, Map, Measure and Manage. NIST added a Generative AI Profile (NIST AI 600-1) on July 26, 2024, and says the framework is being revised under the White House AI Action Plan. For unsanctioned AI use, the Govern and Map functions do most of the work: who decides, and where AI is actually in use.
ISO/IEC 42001:2023, published in December 2023, is the first management system standard for AI. It follows the same structure as ISO/IEC 27001, so a company that already runs an information security program can extend it to AI. Most small businesses will not seek certification, but its idea of an AI inventory with named owners is worth copying.
What shadow AI means under Massachusetts 201 CMR 17.00
If your business holds personal information about Massachusetts residents, shadow AI is also a compliance question. 201 CMR 17.00 requires a written information security program, and section 17.03(2)(f) requires "taking reasonable steps to select and retain third-party service providers that are capable of maintaining appropriate security measures to protect such personal information," and "requiring such third-party service providers by contract to implement and maintain such appropriate security measures."
An AI tool that an employee signed up for on a personal account is a service provider you never selected and have no contract with. If a client's name and account number go into it, the program you wrote does not cover that path. Section 17.03(2)(b) also calls for "ongoing employee (including temporary and contract employee) training," which is a natural home for your AI policy. The guide to Massachusetts AI regulations for business covers the wider picture, and what a data breach costs a Massachusetts business shows why the paperwork matters.
Questions to ask an AI vendor before you sanction it
Moving a tool from shadow AI to approved AI comes down to the answers a vendor gives in writing. These are the questions I would ask about protecting your data, especially when several people or clients work in the same tool:
Does the business plan train models on our prompts or files, and is that off by default?
How long are prompts, outputs and uploads kept, and can we shorten that?
Who at the vendor can read our data, and under what conditions?
Which sub-processors handle our data, and where is it stored?
Can an admin see usage, export logs and remove a user the same day they leave?
What happens to our data when we cancel?
Will the vendor sign terms that meet our obligations, including 201 CMR 17.00 for Massachusetts data?
Shadow AI is the use of AI tools and accounts outside an organization's visibility or policy, usually by employees trying to work faster. Research finds more than 80% of workers use unapproved AI tools, often through personal accounts, which means the practice is widespread and mostly well-intentioned rather than malicious.
Why is banning shadow AI a bad idea?
Because it hides the behavior instead of stopping it. Studies show nearly half of employees would keep using personal AI accounts after a ban, which trades a governable problem for an invisible one. Since shadow-AI-linked breaches carry a cost premium, losing visibility is the opposite of what you want.
How do I govern shadow AI without killing productivity?
Make the sanctioned path easier than the unsanctioned one. Provide approved tools, write a plain-language policy that is permissive about value and strict about data, give people clear guidance on what data goes where, and maintain visibility into actual usage. Govern by enabling rather than forbidding.
Is shadow AI really a security problem or a data problem?
Mostly a data-governance problem. The risk is sensitive data leaving your control, more than the existence of a chatbot. If your data is organized and governed, sanctioning AI is straightforward; if it is scattered across many tools, every new tool multiplies exposure.
What does shadow AI do?
Shadow AI moves company information into AI services the business has not approved: chatbots on personal accounts, browser extensions, note-takers and AI features inside existing apps. It usually helps people work faster, and it also sends data to vendors you have no agreement with, which is where the risk comes from.
Is there an app that blocks shadow AI?
Web filters, DNS filtering, managed browser policies and secure web gateways can block known AI sites. They do not reach personal phones or AI features inside approved tools, and 46% of workers in a Software AG survey said they would keep their own AI tools under a full ban. Blocking works best as one part of a sanctioned lane.
Is there an AI governance framework for shadow AI?
Yes. The NIST AI Risk Management Framework is free and voluntary and organizes the work into Govern, Map, Measure and Manage. ISO/IEC 42001:2023 is the management system standard for AI. A small business can borrow the inventory and ownership ideas from both without seeking certification.
How common is shadow AI in 2026?
It is very common. UpGuard's late 2025 report found more than 80% of workers use unapproved AI tools, and IBM's 2026 Cost of a Data Breach report found shadow AI incidents at 43% of breached organizations, up from 20% the year before, with those breaches averaging USD 5.39 million.
Can a small business govern shadow AI for free?
For the most part, yes. A no-blame survey, a review of admin consoles, a one-page policy and a quarterly check cost time rather than money, and the NIST framework is free. The main spend worth making is business accounts for the approved tools, because their contract terms are what make a tool safe to sanction.
Does shadow AI matter under Massachusetts law?
It can, because 201 CMR 17.00 requires businesses holding Massachusetts residents' personal information to select capable service providers and bind them by contract to protect that information. An AI tool on a personal account has no such contract, so customer data pasted into it falls outside your written security program.
An AI acceptable use policy for small business now has to cover agents that act, not just people who paste. ISACA's May 2026 poll found only 38 percent of organizations had a formal, comprehensive AI policy. Seven parts to write, from approval lines to Massachusetts law.
An AI audit for a business is an inventory plus an evidence check on every AI system in use. IBM's 2026 report found 92 percent of organizations hit by an AI-related breach lacked proper AI access controls. The inventory is where the surprise is.
How to audit AI spending without buying a tool first. Zylo's 2026 index found ChatGPT is now the most expensed app, so the audit starts in card statements and expense reports, then moves to API keys, owners and a monthly review.