How to Evaluate a Technology Partner When You're a Fintech Under $50M ARR
The vendor pitch deck won't tell you what you need to know. Here's what to actually look for in a technology partner, from someone on the other side of the table. Verizon's 2026 DBIR found a third party involved in 48% of breaches.
If you're running a fintech between $10M and $50M ARR and you're evaluating technology partners, the pitch decks all look the same: modern stack, agile methodology, security-first, scalable architecture. Everyone says these things, and almost nobody means all of them.
Here's what actually separates a technology partner who'll help you ship from one who'll burn a quarter and leave you with a codebase you can't maintain.
The short version: a good technology partner for a fintech asks about your regulators before your feature list, walks you through how they build, writes your ownership and exit rights into the contract, and can prove their security controls with evidence you could hand an examiner. The Verizon 2026 Data Breach Investigations Report found a third party involved in 48% of breaches, so the technology partner you pick is part of your own security posture from day one.
Ask which regulations apply to you before anyone proposes an architecture.
Get written evidence for encryption, access control and dependency management.
Put code ownership, data portability and knowledge transfer in the contract.
Agree on breach notice times and an exit plan before you sign.
Review the relationship on a schedule after go-live, sized to its risk.
Ask what they build on before they ask what you need
A technology partner should ask about your regulatory environment before they recommend an architecture. Fintech isn't a normal software category: your architecture comes after your compliance obligations, not the other way around.
If a vendor leads with their preferred tech stack ("we're a React/Node shop" or "we build everything on AWS Lambda"), that's a signal. They're fitting your problem into their toolbox instead of choosing the right tool for your constraints.
The first conversation should cover: What regulatory frameworks apply to your product? Where does customer data reside, and where is it allowed to reside? What audit requirements are on your roadmap in the next 12 months? What's your current compliance posture, and where are the gaps?
Architecture decisions that ignore these constraints create expensive rework later. A payment processing system built without PCI DSS considerations from the start will need significant re-architecture before it can pass certification. A lending platform that stores PII without encryption at rest and column-level access controls will face months of remediation before its first SOC 2 audit.
Strong systems grow from strong foundations. The invisible infrastructure matters more than the visible output, so ask a technology partner about it first.
What a fintech vendor evaluation has to cover under the rules you already follow
A fintech vendor evaluation is the structured check you run on a software, infrastructure or development partner before they touch customer data or money movement. For most fintechs it isn't optional. Several rules already require you to pick partners carefully, bind them by contract and keep checking them, and a technology partner who has worked under these rules will recognize them on the first call.
The FTC Safeguards Rule. Fintechs that aren't banks often fall under the FTC's version of the Gramm-Leach-Bliley Act safeguards. 16 CFR 314.4(f) tells you to oversee service providers by "taking reasonable steps to select and retain service providers that are capable of maintaining appropriate safeguards for the customer information at issue," "requiring your service providers by contract to implement and maintain such safeguards," and "periodically assessing your service providers based on the risk they present and the continued adequacy of their safeguards." The same section requires you to "protect by encryption all customer information held or transmitted by you both in transit over external networks and at rest," and, since May 2024, to notify the FTC within 30 days of discovering a notification event that involves at least 500 consumers. That's why encryption by default is the first security question below.
Massachusetts 201 CMR 17.00. If you hold personal information about Massachusetts residents, 201 CMR 17.03(2)(f) requires "taking reasonable steps to select and retain third-party service providers that are capable of maintaining appropriate security measures" and "requiring such third-party service providers by contract to implement and maintain such appropriate security measures for personal information." I wrote up the rest of that program in what a Massachusetts WISP has to include.
SEC Regulation S-P. If your fintech is a broker-dealer, funding portal, registered investment adviser or transfer agent, the 2024 amendments to Regulation S-P apply. The SEC's small entity compliance guide says your policies must require service providers to notify you "as soon as possible, but no later than 72 hours after becoming aware" of a breach of a customer information system they maintain. Larger entities had to comply by December 3, 2025, and smaller entities by June 3, 2026.
Your bank partner's rules. If you run on a sponsor bank, the bank answers to its regulators for you and for the vendors you bring, under what examiners call third-party risk management. The 2023 Interagency Guidance on Third-Party Relationships from the Federal Reserve, FDIC and OCC lays out a life cycle of planning, due diligence and third-party selection, contract negotiation, ongoing monitoring, and termination. On September 11, 2026 the agencies, joined by the NCUA, proposed replacing that guidance with a more tailored, principles-based version, and the comment period now runs to December 16. Until a final version is out, the 2023 guidance is still what your bank works from, and its five stages are a sound shape for your own process either way.
A technology partner who can talk through these without notes has built for regulated clients before. One who hears them for the first time in your kickoff will be learning on your schedule.
Every vendor has a security slide. It usually says "we follow best practices" and has a lock icon. That tells you nothing.
What you actually want to know:
Do they encrypt data at rest by default, or on request? If encryption is an add-on or a "premium tier" feature, security is a feature they bolt on when clients ask rather than part of how they build.
Can they describe their dependency management process? Third-party libraries are the most common attack surface in modern applications. A partner who reviews dependencies before adoption, monitors for CVEs, and has a documented process for patching critical vulnerabilities is operating at a different level than one who runs Dependabot and hopes for the best.
The numbers back this up. Black Duck's 2026 Open Source Security and Risk Analysis found open source in 98% of the 947 codebases it audited, and the mean number of vulnerabilities per codebase rose 107% from the year before. Verizon's 2026 DBIR found that 31% of breaches started with vulnerability exploitation, the first time in the report's 19 years that it passed stolen credentials as the top way in. Ask the technology partner for the last time they patched a critical CVE in a client system and how long it took from disclosure to deploy.
What does their access control model look like internally? Ask about their own systems as well as your project. Do their developers have production database access? Is there an audit trail for who accessed what? A partner whose own house is organized is more likely to build yours the same way.
Have they been through a client's SOC 2 audit before? That means a client's audit rather than their own SOC 2: they've built systems that passed external audit scrutiny. That experience changes how they architect everything.
It also helps to know what a SOC 2 report is and isn't. It's a CPA firm's examination against the AICPA's Trust Services Criteria, and a Type II report covers how controls worked over a period, not just on one day. Brian has a clear guide to when a small business needs SOC 2 and when a security questionnaire is enough, which is useful on both sides of this conversation. If your technology partner has a report, read the exceptions and the complementary user entity controls, the list of things the report assumes you will do yourself.
Security posture is visible in the details: who can open the cabinet, and whether anyone writes it down.
Vendor lock-in is the most expensive mistake in technology partnerships, and it's almost always invisible at contract signing.
Red flags:
Proprietary frameworks. If the partner builds on their own internal framework that only their team understands, your switching costs are enormous. Hiring that partner means committing to them for the life of the system.
No code ownership clause. You should own the codebase, full stop. If the contract doesn't explicitly state that you own all intellectual property produced during the engagement, walk away. This includes infrastructure-as-code, CI/CD configurations, and deployment scripts, not just application code.
No knowledge transfer plan. A good partner proactively raises knowledge transfer in the commercial conversation. How will your internal team be brought up to speed? What documentation is included? What happens to institutional knowledge when the engagement ends? If these questions aren't discussed before signing, the partner's business model likely depends on you never being able to leave.
No data portability. Your data should be exportable in standard formats at any time. If the system stores data in proprietary structures that require the partner's tools to access, you're locked in by your own data.
Lock-in also builds up through accounts. If the cloud account, the domain, the code repository or the payment processor login sits in the technology partner's name, you're renting your own system. LTFI's guide to how vendor lock-in happens and how to avoid it covers exit fees, closed formats and accounts held in someone else's name, with five questions to ask before you sign. I go through the account side in who owns the site, the host and the login.
One question reveals more than a capabilities deck: "Walk me through the first three decisions you make on a new build."
Ask to see their process, not their portfolio
Case studies tell you what a partner has built. Process tells you how they build, which is what determines whether your engagement will succeed.
Useful questions:
"Walk me through the first three decisions you make on a new engagement." If the answer starts with features, be concerned. If the answer starts with compliance requirements, data architecture, and security boundaries, you can be confident.
"How do you handle a production incident at 2 AM?" You want to hear named people, documented runbooks, and automated alerting, not "we have an on-call rotation" with no detail.
"Show me a recent pull request." You won't see the code itself (that's likely under NDA), but you can see the process around it. Is there a review? Are tests required? Is there a CI/CD gate? The hygiene of the development process reveals more than any slide deck.
"What's the last engagement you turned down, and why?" A partner who says yes to everything is a partner who doesn't specialize. You want someone who understands the boundaries of their competence and isn't afraid to tell you when something is outside their scope.
How to evaluate a technology partner's demo beyond the surface
A demo is built to go well. The useful part is what happens when you step off the script. Ask the presenter to show you an error state, a failed payment, a rejected KYC check or an expired session. Ask them to change one rule live, such as a transaction limit, and show you where that change is logged. Ask who on their side would get paged if the thing you just watched broke in production.
Bring your own data shape. A demo on clean sample data says little about how a system handles your ACH returns, partial refunds or a customer with two legal names. If the technology partner can't run a small test on a sanitized copy of your data before signing, plan a paid discovery phase that does it.
Keep notes as you go. After the demo, list each claim (for example "supports SOC 2 evidence export" or "handles idempotent retries") and mark which ones you watched happen. The unmarked ones become questions for the reference call. My longer list for software demos is in how to evaluate tools without getting sold.
If you have a stack of vendor documents to get through (SOC 2 reports, security questionnaires, master service agreements), a model can help you find what's missing faster. Qurtoo's walkthrough on prompting for supply chain risk in vendor documents shows three prompts that turn contract PDFs into a structured red-flag list. A person still reads the clauses that matter before anyone signs.
The most resilient networks are distributed, redundant, and self-healing, principles that apply to content architecture as much as biology.
The integration test
Fintech systems don't exist in isolation. They connect to payment gateways, KYC providers, core banking platforms, credit bureaus, and regulatory reporting services. Your technology partner needs to demonstrate they understand integration resilience: what happens when a third-party API goes down, times out, or returns unexpected data.
Ask specifically: How do you handle partial failures in multi-step transactions? What's your retry strategy? How do you prevent duplicate transactions during recovery? What monitoring do you have for integration health?
The answers should be specific and technical. If the response is "we handle edge cases as they come up," that describes hope rather than a process.
How to do a vendor evaluation, step by step
The interagency life cycle gives a good order for a fintech of any size. Here it is scaled to a company under $50M ARR choosing a technology partner for one product.
Plan. Write one page on what the technology partner will touch: which systems, which data (card numbers, bank account numbers, Social Security numbers, credit data), which regulators care, and what happens to customers if the partner disappears for a week. That page decides how deep the rest goes.
Shortlist on fit. Drop any technology partner who leads with a stack before asking about your obligations. Keep two or three.
Due diligence. Request the technology partner's SOC 2 Type II report or equivalent, the last penetration test summary, an insurance certificate, a sample incident report with names removed, and two client references in regulated work. Ask the security questions above and the integration questions, in writing.
Contract. Put ownership, data portability, breach notice time, subcontractor approval, audit rights and the exit plan in the agreement. The FTC rule and 201 CMR 17.00 both expect the safeguards themselves to be in the contract.
Monitor. Set a review rhythm that matches the risk. A technology partner with production access to customer data gets a quarterly check; a design agency with no data access gets an annual one.
Plan the exit. Decide now how you'd hand the system from the technology partner to another team or bring it in house, and test the data export once before go-live.
Illustrative example: a lending platform picks a technology partner to build its underwriting service. The plan page shows the partner will see Social Security numbers and bank data for Massachusetts and New York borrowers, so the platform asks for the partner's SOC 2 Type II report, confirms encryption at rest is on by default, writes a 72-hour breach notice into the contract to match its own obligations, and keeps production access with its own staff. That's a few weeks of work, and it's much cheaper than finding out during an audit that nobody can say who touched the data.
Exit terms to put in a technology partner contract
The termination stage is the one teams skip, and it's where switching costs show up. These terms are worth having in writing for any technology partner, and they matter most in payment and core processing contracts where a forced migration can stop money moving.
Transition assistance. A defined period after notice during which the technology partner keeps the system running and helps the next team take over, at rates agreed now.
Data return and deletion. Your data returned in a named, documented format within a set number of days, then deleted, with written confirmation.
Code, credentials and keys. Repositories, infrastructure-as-code, encryption keys, API keys and admin logins handed over, with the partner's own access removed and logged.
Termination for cause and for convenience. The right to leave after a security incident, a failed audit finding that isn't fixed in time, or a change of control at the technology partner.
Subcontractor list. Every party that touches your data, the technology partner's own vendors included, with notice before a new one is added.
How do I evaluate a technology partner's performance after signing?
Evaluating vendor performance means checking the technology partner against the commitments in the contract, on a schedule, with evidence. A one-time review at signing doesn't tell you what changed since. For a fintech technology partner, a quarterly review can cover:
Delivery. Planned work against shipped work, and the defects that reached production.
Incidents. Every incident, how long it took to detect and resolve, and whether the agreed notice time was met.
Patching. Days from a critical vulnerability disclosure to the fix in your systems.
Access. A list of who at the technology partner has access to production and customer data, reviewed and trimmed.
Evidence. A current SOC 2 report or bridge letter, pen test results, and any change in subcontractors.
Knowledge transfer. Whether your team could run the system without the technology partner today, and what documentation is still missing.
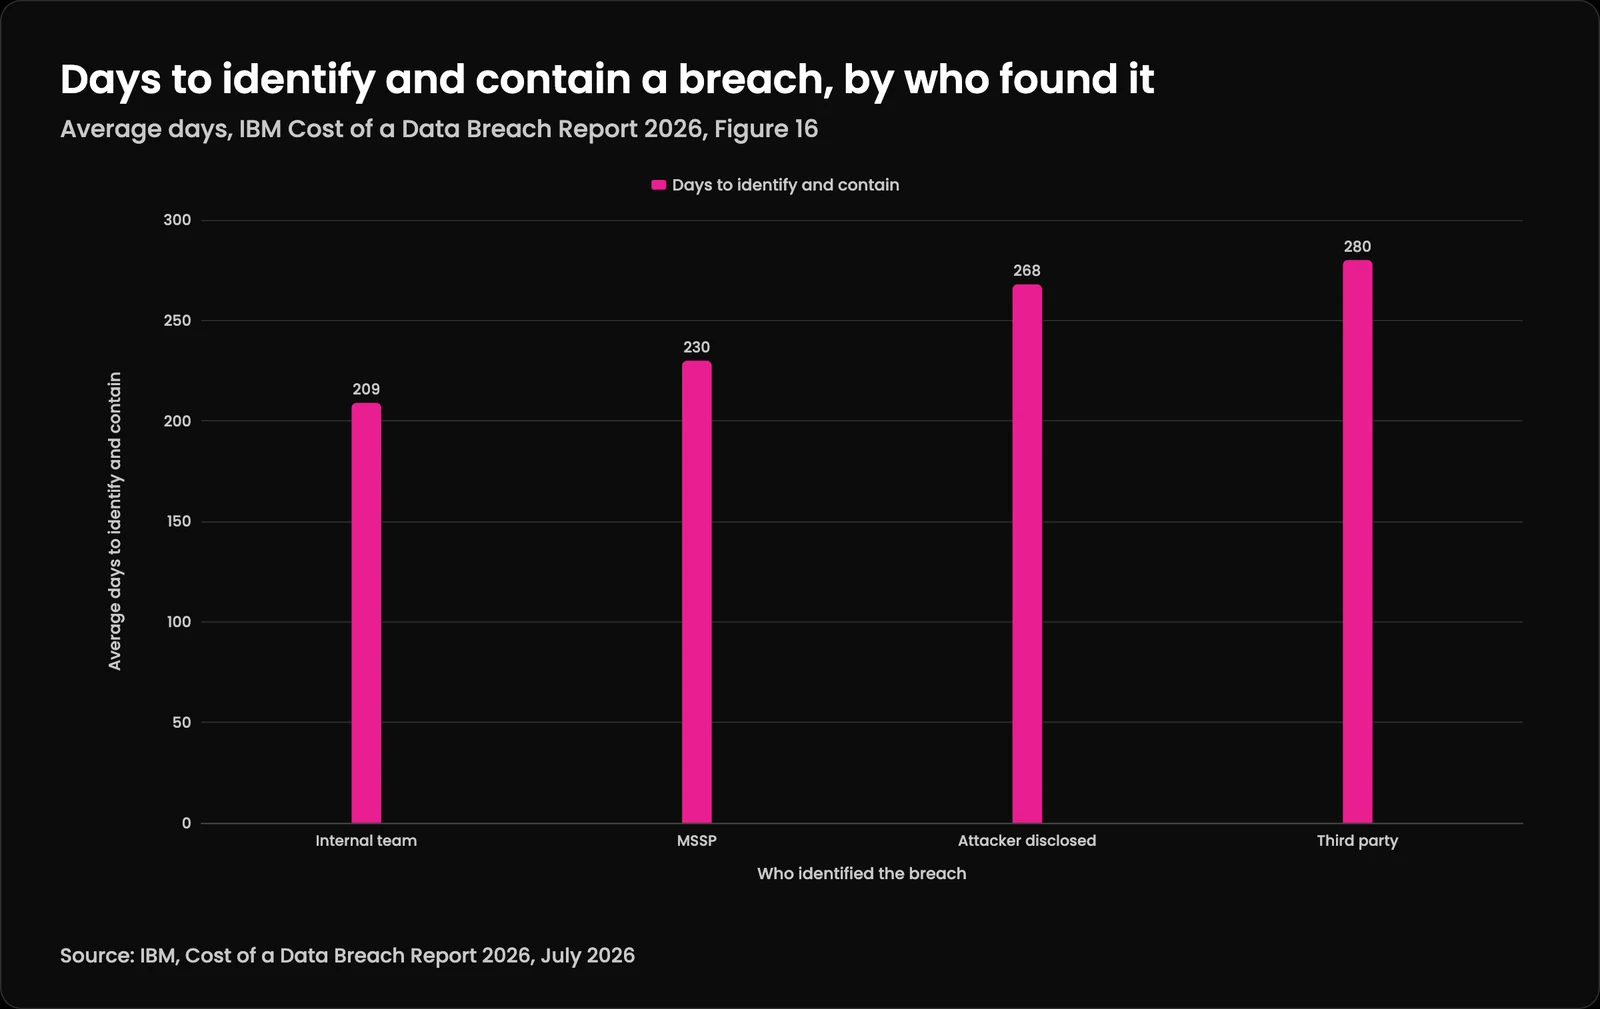
The incident line matters more than it looks. The IBM Cost of a Data Breach 2026 report found breaches took 280 days on average to identify and contain when a third party such as a business partner, consultant or law enforcement found them, 268 days when the attacker disclosed it, 230 days when a managed security service provider found them, and 209 days when an internal security team did. A technology partner who tells you quickly about their own problems shortens that clock.
In IBM's 2026 data, breaches that a third party found took the longest to contain, 280 days against 209 for an internal team.
Days to identify and contain a breach, by who found it (IBM, Cost of a Data Breach Report 2026, July 2026)
Who identified the breach
Days to identify and contain
Internal team
209
MSSP
230
Attacker disclosed
268
Third party
280
Does consolidating vendors into one technology partner save money?
Sometimes, and the savings are easier to promise than to measure. Fewer vendors can mean fewer contracts, fewer security reviews and one set of audit evidence. It can also mean one technology partner holding your code, your hosting and your data, which raises the stakes on everything in the lock-in section. IBM's 2026 report counted security system complexity as one of the factors that most raised breach costs, adding $208,265 to the average, and a supply chain breach through a compromised business partner as the costliest factor, adding $227,250. Both point the same way: simpler is better, as long as that single technology partner is strong.
In a regulated business, plan the transition before you sign. Map each system and the data it holds, decide the order of moves, keep the old vendor under contract until the new setup has passed a test cycle, and keep your auditors informed so evidence doesn't have a gap. Ask the consolidating technology partner to show their savings math line by line, including the cost of the migration itself.
What matters more than technology
The technology stack matters less than most vendors want you to believe. What matters is whether the partner understands your regulatory environment, builds security into the architecture from day one, creates systems you can maintain without them, and communicates honestly about what they can and can't do.
The best technology partners are the ones who make themselves unnecessary over time: transferring knowledge, documenting decisions, and building systems that your internal team can own. If a partner's engagement model requires you to keep paying them forever, that's dependency rather than partnership.
Frequently asked questions about evaluating technology partners in fintech
What's the most important question to ask a technology vendor during evaluation?
"Walk me through the first three decisions you make on a new engagement." The answer reveals whether the vendor leads with compliance and security (good) or features and technology preferences (risky). In fintech, architecture decisions must follow regulatory constraints, not the other way around.
How do I avoid vendor lock-in with a technology partner?
Insist on code ownership in the contract, including infrastructure-as-code and deployment configurations. Require data portability in standard formats. Avoid partners who build on proprietary internal frameworks. Include a knowledge transfer plan in the statement of work. If these items aren't raised by the vendor proactively, proceed with caution.
Should a fintech company prioritize cost or security when choosing a technology partner?
Security. A lower-cost partner who doesn't build security into the architecture will cost more in the long run through audit remediation, incident response, and rework. IBM's 2026 Cost of a Data Breach report ranks a DevSecOps approach, security built into the development lifecycle, as the top factor lowering breach costs, $253,805 below the $4.99 million global average, and that saving belongs in any total cost of ownership comparison.
What compliance frameworks should my technology partner be familiar with?
At minimum for fintech: SOC 2 Type II, PCI DSS (if handling payment data), state money transmitter requirements, SEC cybersecurity disclosure rules (if applicable), and data residency regulations in your operating jurisdictions. A partner who hasn't navigated at least two of these in prior engagements will be learning on your dime.
What is a fintech vendor evaluation?
It's the review a fintech runs before a vendor or technology partner gets access to customer data, money movement or production systems: what the vendor will touch, the evidence for its security controls, the contract terms for ownership, breach notice and exit, and a plan for checking it again after go-live. The FTC Safeguards Rule and 201 CMR 17.00 both expect this kind of selection and contract work.
Does the FTC Safeguards Rule apply to my technology partner?
The rule applies to you if you're a non-bank financial institution under FTC jurisdiction, and it makes you responsible for overseeing your service providers. 16 CFR 314.4(f) requires you to choose providers capable of appropriate safeguards, require those safeguards by contract, and assess providers periodically based on their risk.
What version of PCI DSS should a technology partner build to?
PCI DSS v4.0.1. Its future-dated requirements, including the payment page script controls in 6.4.3 and 11.6.1, became mandatory on 31 March 2025, according to the PCI Security Standards Council.
How quickly should a technology partner tell us about a breach?
Set a time in the contract that leaves you room to meet your own deadlines. Regulation S-P requires covered institutions to make service providers give notice no later than 72 hours after becoming aware of a breach, and the FTC Safeguards Rule gives you 30 days to notify the FTC for events involving 500 or more consumers. Many fintechs use 72 hours or less as the default for every technology partner.
How often should a fintech review a technology partner?
Match it to the risk. A technology partner with production access to customer data or money movement warrants a quarterly review and a full reassessment each year; a low-risk vendor with no data access can be reviewed annually. Review again after any incident, ownership change or major new scope.
Non-compliance cost $14.82 million on average versus $5.47 million to maintain compliance in Ponemon's 2017 study, a 2.71x gap. Compliance engineering means building systems where evidence generates itself instead of assembling it from memory before each audit.
Coalition put average global cyber claim severity at $116,000 for 2025, well under most policy limits. That means cyber insurance exclusions and sublimits, not the limit, decide what you collect.