Vendor Consolidation for Regulated Industries: When Fewer Tools Means Better Compliance
68% of technology leaders plan to consolidate vendors this year. In regulated industries, the compliance case is even stronger than the cost case: vendor consolidation means fewer security reviews, fewer contracts and fewer audit gaps.
The short version: vendor consolidation in a regulated industry is mostly a compliance project that happens to save money. Every vendor you remove is one less security review, one less data processing agreement and one less gap an auditor can find. The savings are real, but the oversight you get back is worth more.
Map where sensitive data flows before you cut anything.
Consolidate by trust boundary, and keep specialist tools where the domain demands them.
Plan the transition: contracts, parallel runs, data return and access removal.
Test the stack after vendor consolidation and write down what changed for your next audit.
Gatekeeper's 2026 procurement data shows that 68% of technology leaders plan to consolidate vendors this year, with most targeting a 20% reduction in vendor count (Gatekeeper, January 2026, citing CIO research). But in regulated industries (fintech, healthcare, cannabis, legal tech), the compliance argument for consolidation is stronger than the cost argument.
Every vendor in your stack is an attack surface, a compliance dependency, and a line item on your next audit questionnaire. Fewer vendors doesn't just save money. It reduces the number of things that can go wrong when a regulator asks for evidence. Technology fragmentation compounds (across integration maintenance, incident response coordination, and vendor oversight) in ways that the original per-seat savings never account for.
Why does vendor consolidation matter more in regulated industries?
When an auditor evaluates your information security program, one of the first things they assess is your vendor management posture. Every third-party tool with access to sensitive data triggers a set of questions: What data do they process? Where is it stored? What's their incident response process? Do they have their own SOC 2? When was their last penetration test?
With 40 vendors, that's 40 sets of due diligence questionnaires, 40 contracts to review for data processing terms, 40 potential points of failure in your compliance posture. With 15, the surface area shrinks dramatically, and the depth of oversight you can maintain on each remaining vendor increases proportionally.
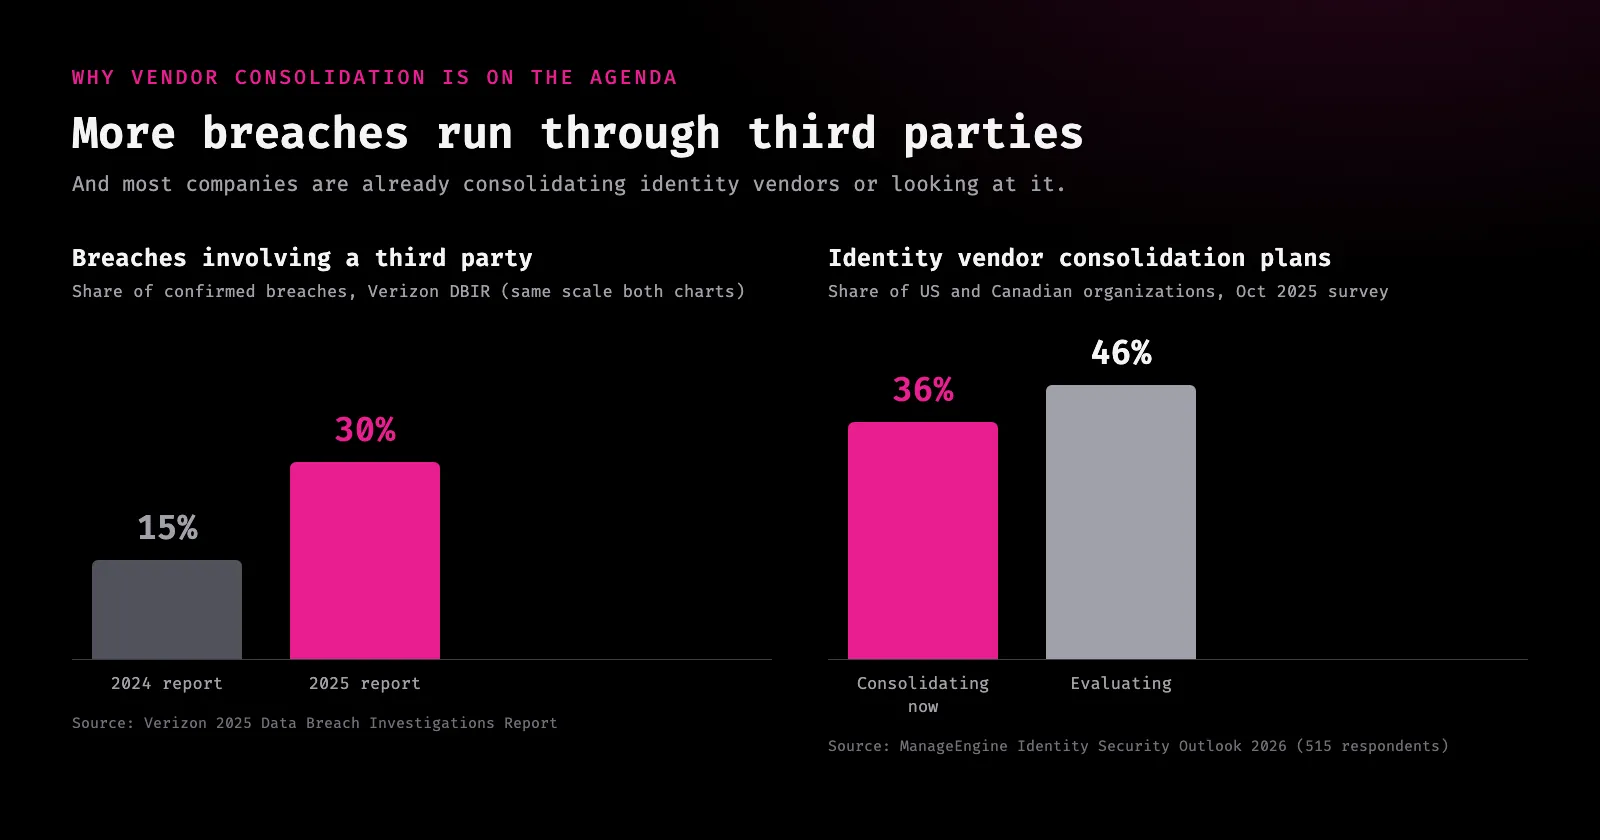
The breach data points the same way. Verizon's 2025 Data Breach Investigations Report found that the share of breaches involving a third party doubled from 15% to 30% in a single year. Each vendor you keep is a relationship you have to watch, so vendor consolidation is one of the few security moves that shrinks the watch list instead of adding to it.
Third-party involvement in breaches doubled to 30% (Verizon DBIR 2025), and 82% of organizations are consolidating identity vendors or evaluating it (ManageEngine Identity Security Outlook 2026).
Identity is where the overlap shows first. ManageEngine's Identity Security Outlook 2026 found that nearly three in four US organizations run a fragmented identity and access stack, and 82% are consolidating identity vendors or evaluating it. The evidence gaps auditors flag often trace back to siloed enforcement across disconnected tools. When your identity management, logging, and access control are spread across eight vendors with different permission models, proving consistent policy enforcement becomes a research project instead of a report.
Fewer vendors means fewer places your data lives, and each one you keep can be documented and reviewed properly.
What vendor consolidation actually looks like
Consolidation isn't ripping out every tool and replacing them with a single platform. That's a different risk, concentration risk, and it's just as dangerous as sprawl.
Effective consolidation follows a framework:
Map the data flows first. Before you cut any vendor, document where sensitive data enters your stack, where it moves, and where it rests. Before adding any vendor, run the same evaluation in reverse: vendor due diligence (data handling, contractual terms, security posture, support model) determines whether a new addition belongs in the stack at all. You'll often find that three tools process the same customer data in slightly different ways, with slightly different security postures. That overlap is where consolidation creates the most value, both operationally and for compliance. A security architecture review produces this map as a document you can hand to an auditor.
Consolidate by trust boundary, not by function. The goal isn't "one tool per category." It's "fewer trust boundaries for sensitive data." If your CRM, your email marketing platform, and your support tool all have access to customer PII, consolidating to a platform that handles all three means one vendor agreement, one security review, one data processing addendum, instead of three. Each of those tools also brings its own sub-processors, so the real count of parties touching the data is higher than your vendor list shows.
Keep best-of-breed where the domain requires it. Your payment processor, your KYC provider, and your core banking integration are specialized tools that exist because the domain demands them. Don't consolidate those. Consolidate the layer around them: the operational tools, the analytics, the workflow automation, the internal dashboards.
Test integration integrity, not just feature parity. When you move from three vendors to one, the replacement needs to handle the edge cases the specialized tools handled. FinTech Global's March 2026 analysis warned that "consolidation does not automatically equal integration," since acquired capabilities may retain different data models and disconnected interfaces. Verify that the consolidated platform actually unifies the data, not just the billing.
Every vendor that stays after consolidation needs a current contract with data processing, breach notice and exit terms that match how you use it today.
Vendor consolidation transition planning: moving without a compliance gap
Most of the risk in vendor consolidation sits in the move itself. For a few weeks, data lives in two places, two sets of people have access, and the audit trail is split between an old system and a new one. Planning the transition is what keeps that window short and documented.
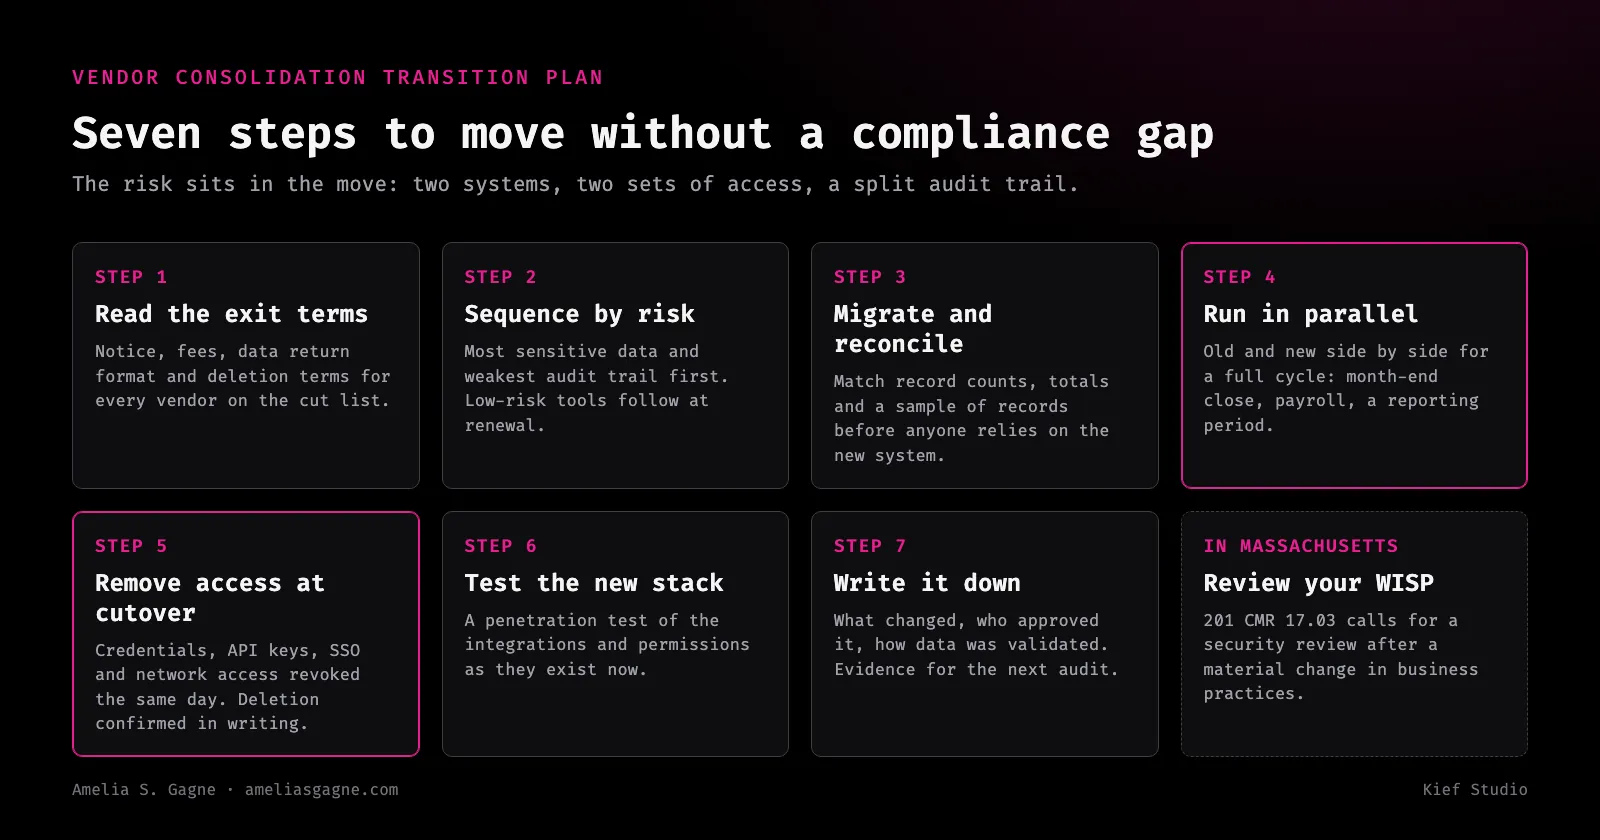
A vendor consolidation transition plan in seven steps. The parallel run and the cutover are where data sits in two places, so they get the most attention.
Step 1: Read the exit terms before you announce anything
Your current contracts decide what leaving costs: notice periods, termination fees, how long the vendor keeps your data, and in what format they hand it back. The 2023 Interagency Guidance on Third-Party Relationships from the Federal Reserve, FDIC and OCC treats termination as its own stage of the vendor life cycle, covering costs, data retention and destruction, and system connections that need watching after the relationship ends. The exit terms that decide what leaving costs are worth pulling for every vendor on the cut list.
Step 2: Sequence by risk, not by renewal date
It's tempting to cut whichever contract renews next. A better order for vendor consolidation moves the vendors with the most sensitive data and the weakest audit trail first, because that's where the compliance gain is largest. Low-risk tools can follow on their natural renewal dates.
Step 3: Migrate the data and prove it arrived intact
Export from the old system, load into the new one, then reconcile record counts, totals and a sample of individual records before anyone relies on the new platform. A migration you haven't reconciled is a migration you can't defend to an auditor. For larger moves, data engineering work (mapping fields, transforming formats, keeping a log of every load) is usually the longest part of the project.
Step 4: Run both systems in parallel for a full cycle
During vendor consolidation, keep the old and new systems running side by side through at least one complete business cycle: a month-end close, a payroll run, a reporting period. Differences that show up in parallel are cheap to fix. Differences that show up after the old vendor is gone are expensive.
Step 5: Remove access the day you cut over
Revoke the old vendor's credentials, API keys, single sign-on connections and any network access on cutover day, then confirm in writing that they've returned or destroyed your data as the contract requires. Orphaned integrations are one of the quieter ways a vendor consolidation project leaves the stack less secure than it found it.
Step 6: Test the stack after vendor consolidation
A new platform with broader access to your data is a new target. A penetration test after cutover checks the integrations, permissions and exposed services as they actually exist now, rather than as the vendor's documentation describes them. Ongoing vulnerability management keeps that picture current between tests.
Step 7: Write it down for your next audit
Record what changed, when, who approved it, how the data was validated, and what the old vendor confirmed about deletion. That record turns vendor consolidation from a question an auditor asks into evidence you hand over.
Vendor consolidation for fund accounting and other regulated records
Financial records raise the stakes on steps 3 and 4. Fund accounting systems, general ledgers and investor records carry retention rules that outlive the vendor. SEC Rule 204-2 requires investment advisers to keep most books and records for five years from the end of the fiscal year of the last entry, the first two in an appropriate office, so historical data has to stay retrievable after the old system is switched off. Parallel runs for fund accounting should span at least one full period close, with reconciled balances signed off before cutover.
Advisers, broker-dealers and funds also have a newer obligation. The SEC's 2024 amendments to Regulation S-P require written procedures to oversee service providers, including a requirement that they report a breach of customer information within 72 hours of becoming aware of it. Compliance dates passed on December 3, 2025 for larger entities and June 3, 2026 for smaller ones. Every vendor you keep after vendor consolidation needs that clause, and fewer vendors means fewer contracts to amend. The same logic applies to 401(k) technology vendors and anyone else handling participant data.
68% of technology leaders plan to consolidate vendors (Gatekeeper, 2026). Fewer vendors means fewer due diligence questionnaires, fewer data processing agreements, and a smaller attack surface.
What do regulators expect from vendor oversight?
The rules differ by industry, but their third-party risk management requirements ask for the same three things: choose vendors that can protect the data, bind them by contract, and keep checking.
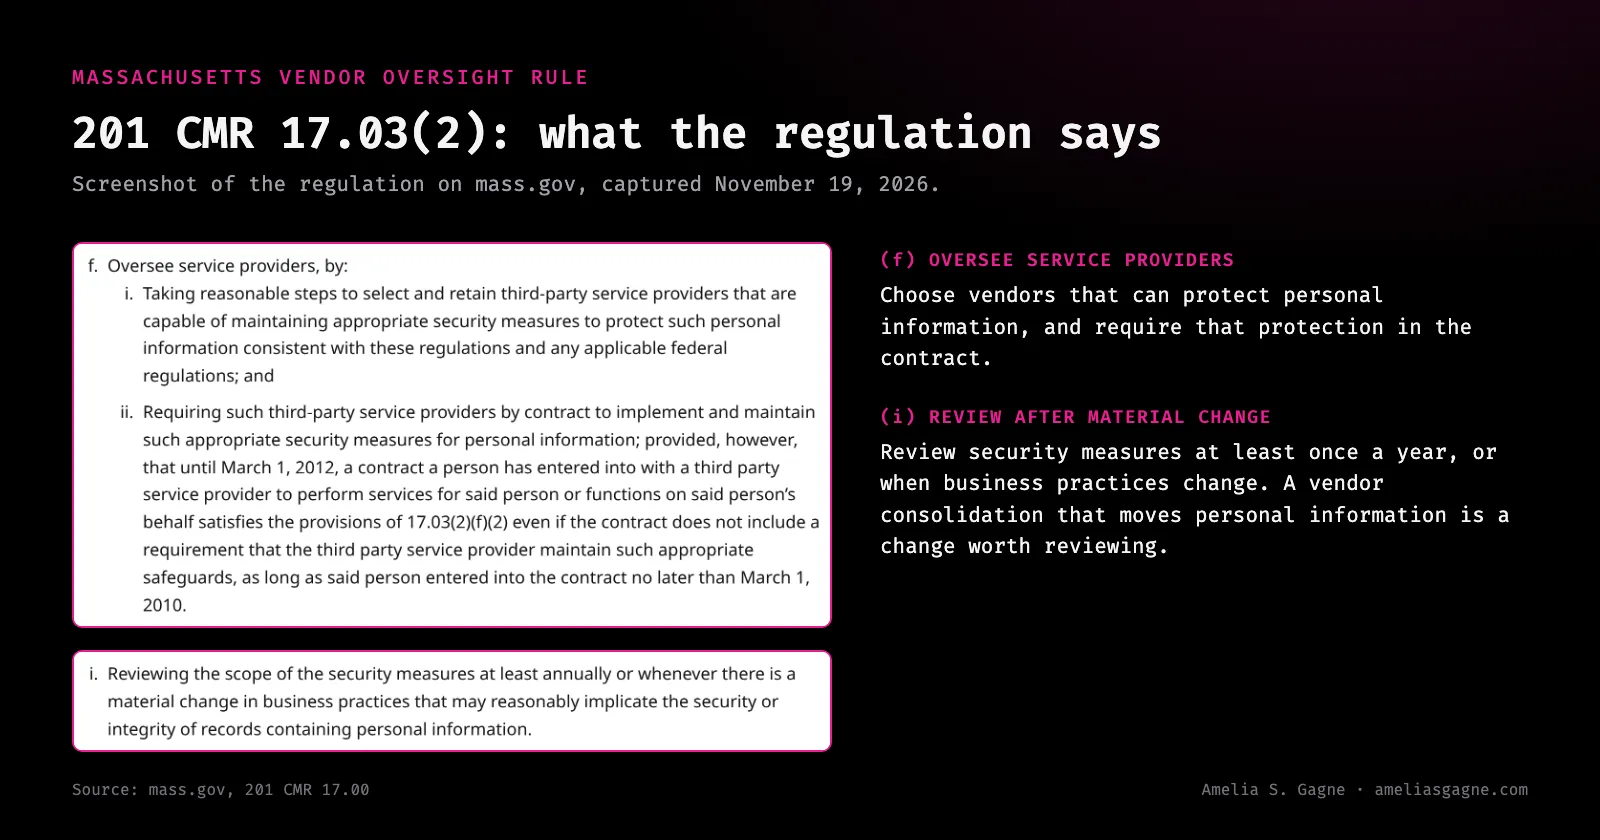
Massachusetts. Under 201 CMR 17.03(2)(f), any business holding personal information about Massachusetts residents must take reasonable steps to select and retain service providers capable of protecting it, and must require those protections by contract. The same section requires reviewing your security measures at least annually or whenever there's a material change in business practices. A vendor consolidation that moves personal information to a new platform is a good reason to run that review and update your written information security program.
The Massachusetts rule on overseeing service providers, 201 CMR 17.03(2)(f), and the review requirement in 17.03(2)(i), as published on mass.gov (captured November 19, 2026).
Banking and lending. The 2023 interagency guidance covers the whole vendor life cycle (planning, due diligence, contract negotiation, ongoing monitoring and termination) and scales expectations to how critical the activity is.
Investment advisers and broker-dealers. Regulation S-P's service provider oversight and 72-hour notice requirement, plus Rule 204-2's recordkeeping, as covered above.
Healthcare. HIPAA requires a business associate agreement with every vendor that handles protected health information. Each vendor you consolidate away is one less agreement to negotiate, track and renew.
In every case, fewer vendors make each of these obligations easier to meet well. That's the practical reason vendor consolidation and security work belong in the same plan.
The risks of over-consolidation
There's a floor to how far you should consolidate, and regulated industries hit it sooner than most.
Concentration risk. If your entire compliance stack runs on one vendor and that vendor has a major incident, your business continuity plan needs to account for a scenario where you lose everything simultaneously. Auditors increasingly ask about single-vendor dependency as a risk factor.
Roadmap dependency. When you consolidate onto a platform, you're betting on their product roadmap aligning with your regulatory needs for the foreseeable future. If they deprioritize a compliance feature you depend on, your options are limited.
Migration cost as switching cost. The deeper you consolidate, the more expensive it becomes to leave. This isn't inherently bad, but it should be a conscious decision, not an accidental one. Factor migration cost into the total cost of ownership for any vendor consolidation decision. Kief Studio's guide to vendor lock-in covers the contract and data-format choices that keep leaving possible.
A practical framework for the vendor consolidation audit
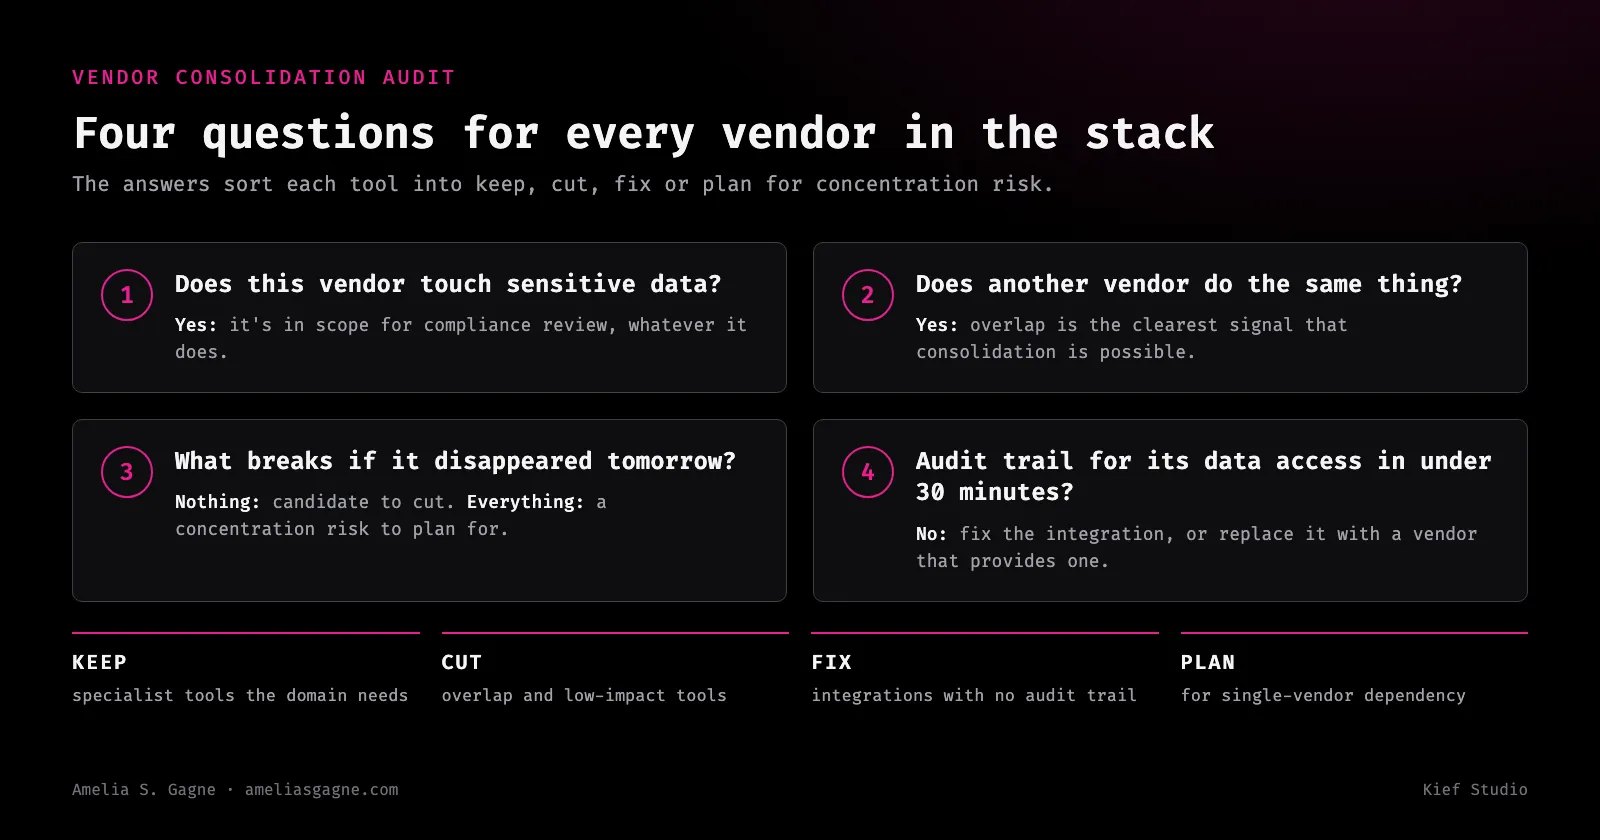
For each vendor in your current stack, answer four questions:
Does this vendor touch sensitive data? If yes, it's in scope for compliance review regardless of what it does.
Is there another vendor in the stack that does the same thing? Overlap is the clearest signal that consolidation is possible.
What would break if this vendor disappeared tomorrow? If the answer is "nothing significant," it's a candidate for elimination. If the answer is "everything," you have a concentration risk to address.
Can you produce a complete audit trail for this vendor's data access in under 30 minutes? If not, the vendor's integration with your compliance program is insufficient. Either fix the integration or replace the vendor with one that provides it.
The four questions sort every tool into keep, cut, fix or plan for concentration risk.
The 20% vendor reduction most teams aim for isn't a target to force. It's what typically falls out of this analysis. Most companies have accumulated tools through years of individual team decisions, each solving a local problem without evaluating the system-wide compliance impact. The audit reveals what's redundant, what's risky, and what's essential. When you run it, the security questions to ask each vendor give you the evidence for question four.
After vendor consolidation, each connection that remains carries more weight, so each one gets a full review, a current contract and a complete audit trail.
Where LTFI fits in a vendor consolidation plan
Disclosure first: Kief Studio, which I co-own, builds and runs LTFI, so read this section with that in mind.
For most small and mid-sized teams, vendor consolidation starts in the operational layer, because that's where the overlap is. A CRM, a project tool, a content calendar, a website editor and a few chat threads each hold part of the customer record, and each is its own vendor review. LTFI puts customers, projects, content and sites in one system, which is the "consolidate by trust boundary" idea applied to everyday operations.
A few details matter for regulated teams in particular:
One audit trail. Every action by people and AI staff is recorded in one log, newest first, which helps with question four of the audit above.
A dedicated server per company. Your company's data sits on its own server, which Kief Studio hosts, patches and watches, so there's one hosting relationship to review instead of several.
AI on keys you own. The AI runs under your own contract with the AI company, so that relationship is yours to review and end.
It doesn't replace the specialist tools this article says to keep. Your payment processor, KYC provider and core banking integration stay where they are, and LTFI connects to many existing tools directly or through their public APIs.
What stays after vendor consolidation
The vendors that survive a consolidation audit are the ones that do three things well: they handle a specific domain that can't be generalized, they provide complete audit trails for data access, and they integrate cleanly with your identity and access management layer.
Everything else is a candidate for replacement, elimination, or absorption into a more capable platform. The compliance posture that results (fewer vendors, deeper oversight, consistent policy enforcement) is what auditors want to see, what regulators expect, and what actually reduces your organization's risk surface.
Frequently asked questions about vendor consolidation for regulated industries
What is vendor consolidation?
Vendor consolidation is the process of reducing the number of third-party tools and services in your technology stack by replacing overlapping capabilities with fewer, more integrated solutions. For regulated industries, the primary benefit is compliance simplification: fewer vendors means fewer due diligence questionnaires, fewer data processing agreements, and a smaller attack surface.
What does vendor consolidation actually cost to implement?
The ROI calculation (what running four specialized vendors actually costs versus one integrated partner, accounting for coordination overhead, context-switching, and integration maintenance) is quantified in one vendor vs. four: the coordination cost.
How many vendors should a mid-market company have?
There's no universal number. The right count depends on your regulatory requirements and the complexity of your operations. Gatekeeper's 2026 figures show most organizations aiming for a 20% reduction. The goal isn't a specific number. It's ensuring every remaining vendor has a clear purpose, proper oversight, and documented data handling.
Does vendor consolidation conflict with best-of-breed strategy?
Not necessarily. The best approach keeps specialized tools where the domain requires them (payment processing, KYC, core banking) and consolidates the operational layer: workflow tools, analytics, dashboards, internal communication. Consolidate by trust boundary, not by function.
What's the biggest risk of vendor consolidation?
Concentration risk. If you consolidate too aggressively onto a single platform, a major incident at that vendor affects your entire operation. The mitigating factor is maintaining documented business continuity plans and ensuring critical data remains exportable in standard formats at all times.
How do you plan a vendor consolidation transition without a compliance gap?
Read the exit terms first, sequence the cuts by data sensitivity, migrate and reconcile the data, run old and new systems in parallel through a full business cycle, revoke the old vendor's access on cutover day, test the new stack, and document each step for your next audit.
Does vendor consolidation count as a material change under 201 CMR 17.00?
201 CMR 17.03 requires reviewing your security measures at least annually or whenever a material change in business practices could affect the security of personal information. Moving Massachusetts residents' personal information to a new vendor is the kind of change that calls for that review and an update to your WISP.
How long should old and new systems run in parallel during vendor consolidation?
At least one complete business cycle, such as a month-end close, a payroll run or a reporting period, so every recurring process runs once on both systems. For fund accounting, that means at least one full period close with reconciled balances before cutover.
What happens to your data after you remove a vendor?
That depends on the contract. Check the data return and destruction terms, request an export in a standard format, and get written confirmation that copies have been deleted. Records with retention requirements, such as those under SEC Rule 204-2, have to stay retrievable after the old system is switched off.
Should you run a penetration test after vendor consolidation?
Yes. Consolidation changes your integrations, permissions and exposed services, and often gives one platform broader access to sensitive data. A penetration test after cutover checks the stack as it now exists.
Is vendor consolidation worth it for a small business?
Often more than for a large one. A small team has less time to review vendors, so each tool it removes frees a larger share of its oversight capacity. Massachusetts small businesses holding residents' personal information carry the same vendor oversight duty under 201 CMR 17.00 as larger companies.
What are the benefits of vendor consolidation?
For a regulated business, vendor consolidation means fewer security reviews, contracts and data processing agreements to maintain, a smaller list of third parties with access to sensitive data, and audit evidence that lives in fewer places. Cost savings come on top of that.
What are the steps of vendor consolidation?
Inventory every vendor and map where sensitive data flows, run the four-question audit, choose which vendors to cut by risk, read the exit terms, migrate and reconcile the data, run old and new systems in parallel, remove the old vendor's access, test the new stack, and document the change for your next audit.
Who should own vendor consolidation in a small company?
One named person, usually whoever already owns compliance or operations, with sign-off from leadership on the cut list. Vendor consolidation touches contracts, data and security at once, so it works best when one person tracks every step and keeps the audit record.
Can one platform replace several operational tools during vendor consolidation?
For the operational layer, often yes. Systems like LTFI combine contacts, projects, content and websites with one audit log, while specialist tools such as payment processing and KYC stay separate. Check that a combined platform really shares one set of data across its features.
How does vendor consolidation affect cyber insurance?
Insurers ask about third-party access and vendor controls on renewal applications. A shorter vendor list with current contracts and documented reviews is easier to answer accurately. What a cyber insurance renewal application asks now covers the questions in detail.
CISA Secure by Demand (August 2024) is the buyer list: is MFA extra, do default passwords still exist, how do patches install, is there a public VDP. Design is the maker pledge. Demand is what you ask before you sign.
Questions to ask business internet providers about cybersecurity: who can change routing, which logs you can export, the incident clock, MFA on the portal, and credits that land on the invoice. CISA's Demand guide is the shopping list. Get it in writing.
Your vendor's security posture is part of your security posture. When they have access to your systems, your data, or your clients — their breach is your breach.