Cyber Insurance Exclusions That Decide Claims
Coalition put average global cyber claim severity at $116,000 for 2025, well under most policy limits. That means cyber insurance exclusions and sublimits, not the limit, decide what you collect.


How to back up a business against ransomware is a restore you have run. FBI (27 Jan 2026) and CISA #StopRansomware: three copies, one offline and immutable, then test. NIST SP 800-34 Rev. 1 treats testing as a step.
How to back up a business against ransomware is a restore you have already run, not a folder named Backup. The FBI's ten actions for cyber resiliency (updated 27 January 2026) says keep at least three copies of critical data on two media types, with one stored offline and immutable, then test restoration. CISA's #StopRansomware Guide (September 2023, still the live page) says offline, encrypted backups, tested in a recovery scenario. NIST SP 800-34 Rev. 1 treats testing as a step. If you cannot name the date of your last restore, you can't yet count on that backup.
The short version: how to back up a business against ransomware comes down to three copies of what you need to run the business, on two kinds of storage, with one copy offline or immutable where ransomware can't reach it. Then restore from it on a schedule and write down how long it took. Sophos's State of Ransomware 2026 found that 66% of organizations whose data was encrypted got it back from backups, up 12 points from the year before.
But here's the part that doesn't get enough attention: businesses with proper backups are far less likely to pay the ransom. They restore from a clean copy and move on. The entire ransomware model collapses when your data exists somewhere the attacker can't reach.
The steps are well known, and most businesses simply don't practice them often enough.
The 3-2-1 rule has been the standard since before ransomware was a household word, and it still works because the logic is sound:
The reasoning behind each number is about eliminating single points of failure. One backup can fail. Two backups on the same drive die together. A backup sitting on the same network as your production systems can be encrypted by the same ransomware that hit everything else. CISA's ransomware guide specifically warns about this.
The offsite copy is your insurance policy. It's the one that survives when everything on your network is compromised. If you take nothing else from this article, take this: at least one backup must live somewhere your primary network cannot reach.
A lot of people search for the exact wording in CISA's guide, because it's the plainest official answer to how to back up a business against ransomware. Part 1 of the #StopRansomware Guide, the preparation section written by CISA with the FBI, NSA and MS-ISAC, tells organizations to "Maintain offline, encrypted backups of critical data" and to "regularly test the availability and integrity of backups in a disaster recovery scenario."
The same section adds two items that small businesses tend to miss. It says to "Maintain and regularly update 'golden images' of critical systems," meaning a clean, ready-to-deploy copy of a configured server or laptop. For cloud resources, it says to use infrastructure as code and to "keep backups of template files offline to quickly redeploy resources." In practice that means the scripts or templates that build your cloud setup belong in the offline backup too.
Each word in that first line does work. Offline means ransomware running on your network can't reach the copy. Encrypted means a stolen backup drive doesn't become a data breach of its own. Tested means someone has restored from it in conditions close to a real incident, which is the step the FBI also puts in its title: action six of its ten actions is "Maintain offline, immutable backups and test restoration."
Most people think of backups as "my documents and photos." That's the floor, not the ceiling. A business backup that lets you actually recover needs to include:
A useful test: if your office burned down tomorrow and you had to set up on new hardware, could you get back to operational from your backups alone? If the answer involves "well, I'd need to call someone to get..." then that thing needs to be in the backup.
The right backup frequency depends on how much work you can afford to lose. This is called your Recovery Point Objective (RPO), and the calculation is straightforward: if you back up nightly and get hit at 4 PM, you lose a full day's work. If that's acceptable, nightly is fine. If losing a day's work means re-entering 200 client records, you need more frequent snapshots.
RPO has a partner, the Recovery Time Objective (RTO), which is how long you can be down. The two numbers pull in different directions on cost, and this explainer on RTO vs RPO walks through how to set each one for a small business.
Practical guidance for most small businesses:
Automated is the operative word. Manual backup processes are backup processes that stop happening the first week someone gets busy. Every modern backup tool supports scheduling, so turn it on.
This isn't an either/or decision. Cloud and local backups solve different problems:
Local backups (external drives, NAS devices) give you fast restore times. If you need to recover a 50 GB database, pulling it from a drive on your desk takes minutes. Pulling it from the cloud takes hours. Local backups also don't depend on internet connectivity.
Cloud backups give you geographic separation. A fire, flood, or theft that destroys your office won't touch your cloud backup. Cloud storage is also harder for ransomware to reach, particularly if it uses immutable storage, which prevents existing files from being modified or deleted for a set retention period.
The 3-2-1 rule accommodates both. Local drive for speed, cloud for disaster resilience. If you only pick one, pick cloud: the offsite copy is the one that saves you from ransomware scenarios where the attacker has been on your network for weeks before triggering the encryption.
The strategy the FBI and CISA describe for how to back up a business against ransomware is 3-2-1 with one copy that ransomware can't change, plus restore testing. What makes that copy safe is less about the brand of storage and more about three settings.
The backup server itself is a target, and it needs patching like anything else. LTFI's write-up on a week of critical backup server flaws covers why keeping the backup server off the everyday domain and patched quickly matters as much as the copies on it.
No single place is safest, which is the point of 3-2-1. The safest arrangement is one copy close by for fast restores, and one copy somewhere a compromised account on your network can't alter: immutable cloud storage, or a drive that's unplugged and locked away between runs.
For Massachusetts businesses, how to back up a business against ransomware is also a legal question, because where you keep the offline drive matters. If the backup holds personal information about Massachusetts residents, 201 CMR 17.00 applies to it. Section 17.03(2)(g) calls for "Reasonable restrictions upon physical access to records containing personal information, and storage of such records and data in locked facilities, storage areas or containers." Section 17.04(5) requires "Encryption of all personal information stored on laptops or other portable devices," and a USB backup drive is a portable device. A rotated, encrypted drive in a locked safe meets both; an unencrypted drive in an unlocked desk drawer meets neither.
Backups belong in the written information security program, too. Section 17.03(2)(i) requires reviewing the scope of security measures "at least annually or whenever there is a material change in business practices." This guide to Massachusetts WISP requirements under 201 CMR 17 covers what the program has to contain.
A backup you've never tested is a backup you're hoping works. Hope is not a recovery strategy.
Veeam's data protection research has tracked this gap for years, and its newest edition, the Data Trust and Resilience Report 2026 (14 April 2026), found that only 28% of organizations hit by ransomware fully recovered all affected data. Another 44% got back less than three quarters of it. The backup ran every night, the logs looked clean, and when it was actually needed, the data was incomplete, corrupted, or in a format nobody could use.
Testing means actually performing a restore, not just checking that the backup job completed. At minimum, quarterly:
Document the results. If the restore took six hours and your business can't survive six hours of downtime, you need a faster restore path: a local backup, a hot standby, or a simpler system architecture. This is exactly the kind of information you want before an incident, not during one. Knowing what the first 48 hours of a breach look like makes it clear why "figure it out during the crisis" isn't a plan.
NIST frames testing the same way. Step six of the seven-step process in SP 800-34 Rev. 1 is "Ensure plan testing, training, and exercises," and the guide explains that "Testing validates recovery capabilities, whereas training prepares recovery personnel for plan activation and exercising the plan identifies planning gaps." A restore test checks the data, and a tabletop exercise checks whether people know their part. Small businesses need both, and the second one can be an hour around a conference table. Any written plan for how to back up a business against ransomware should name who runs the restore test and who sits in on the tabletop.
A restore can bring the attacker back with it. CISA's guide warns that attackers often leave a dropper behind, and that "Care must be taken to identify such dropper malware before rebuilding from backups to prevent continuing compromises." So the question people ask, which tools can verify a backup is clean after a ransomware attack, comes down to a process more than a product. It is the part of how to back up a business against ransomware that only matters on the worst day, so write it down before that day.
Many backup products now include malware scanning of restore points and isolated recovery areas. Those features help, and they still depend on someone knowing when the intrusion began.
Ransomware was a blunt instrument. Attackers would encrypt everything they could reach, as fast as possible, and hope the damage was extensive enough to force payment. Backup strategies designed around this (offsite copies, network segmentation, regular rotation) were effective because the attack was indiscriminate. If your backup was separate from your network, it survived.
AI-augmented ransomware changes the calculus. Modern variants can identify your most valuable files before encrypting, prioritizing databases, financial records, and client data over stock photos and old meeting notes. More critically, AI-driven attacks can detect and target backup connections themselves, identifying mounted backup drives, cloud sync agents, and shadow copies, then deleting or encrypting them before the primary attack begins.
The CISA #StopRansomware Guide warns that "many ransomware variants attempt to find and subsequently delete or encrypt accessible backups." The encryption of production data is the second step, once the safety net is gone.
Survey data backs this up. In Sophos's study of compromised backups and ransomware outcomes (2,974 organizations hit by ransomware, surveyed in early 2024), 94% said attackers tried to compromise their backups, and 57% of those attempts succeeded.
The defense hasn't changed in principle, but it's gotten more specific: air-gapped backups. An air-gapped backup is one that is physically or logically disconnected from your network except during the backup window. A USB drive that you plug in for the backup and unplug when it's done. A cloud backup that uses write-only credentials (the backup agent can upload but can't delete or modify existing backups). Immutable storage that rejects deletion requests for a set retention period, regardless of who (or what) makes the request.
AI also works on the defensive side. Backup monitoring tools now use anomaly detection to flag unusual patterns: a sudden spike in file modifications (which often precedes encryption), backup sizes that shrink unexpectedly (suggesting files were deleted before the backup ran), or backup jobs that start failing after months of clean runs. These early warnings can be the difference between catching ransomware in its staging phase and discovering it after everything is encrypted.
Language models help after an alert, too, if they're given tight instructions and a person reviews the output. This guide to incident response prompts that speed up triage shows how to structure alert triage and timeline reconstruction so the model flags uncertainty instead of guessing.
The principle is the same as it was before AI entered the picture: your last line of defense must exist somewhere the attacker cannot reach. AI just made "cannot reach" a higher bar to clear.
Start by isolating affected systems. The first step on CISA's response checklist is to "Determine which systems were impacted, and immediately isolate them." Pull network cables, turn off Wi-Fi on affected machines, and disconnect shared drives. CISA adds that you should "Power down devices if you are unable to disconnect them from the network," with the caution that powering down can destroy evidence held in memory, so disconnecting is better when you can.
Knowing how to back up a business against ransomware includes knowing what to do with those backups in the first hour:
Modern ransomware usually copies data before encrypting it. If personal information about Massachusetts residents was taken, M.G.L. c. 93H, section 3 requires notice to the Attorney General, the Director of Consumer Affairs and Business Regulation, and the affected residents "as soon as practicable and without unreasonable delay." Brian Gagne's 24-hour plan for a hacked small business website walks through those first hours, including restoring from a clean backup and the 93H notice.
For most organizations, days to weeks. Sophos's 2026 survey release reported that 55% of organizations fully recovered within one week, and 16% in less than a day. That leaves 45% still recovering after a week.
Backups make a measurable difference. In Sophos's 2024 study, 46% of organizations with intact backups were fully recovered within a week, against 26% of those whose backups were compromised. The restore time you measured in your last test is the best predictor you have of where you'd land.
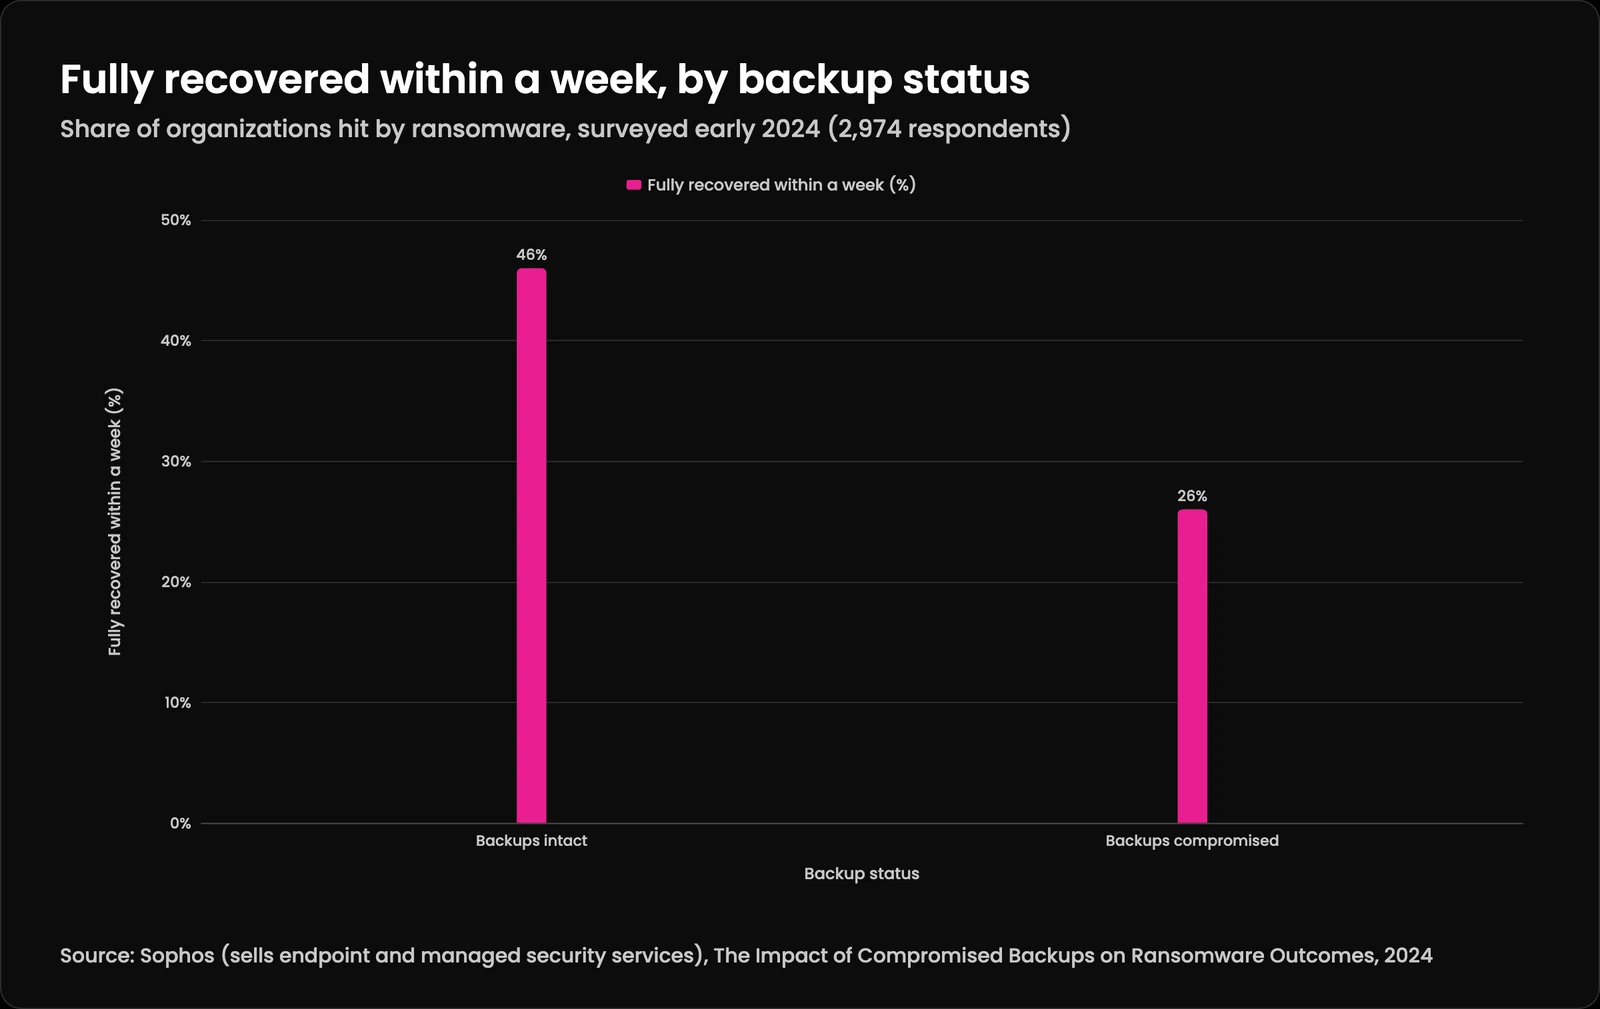
| Backup status | Fully recovered within a week (%) |
|---|---|
| Backups intact | 46% |
| Backups compromised | 26% |
The options get narrower and more expensive, and they're the best argument for learning how to back up a business against ransomware before you need it.
Yes, by a wide margin. Sophos's 2026 report put the average cost of recovering from a ransomware attack, not counting any ransom, at $1.7 million, up 11% from the year before. Its 2024 study split the numbers by backup status: the median recovery cost was $375,000 for organizations whose backups stayed intact, and $3,000,000 for those whose backups were compromised. Organizations with compromised backups also paid the ransom far more often, 67% against 36%.
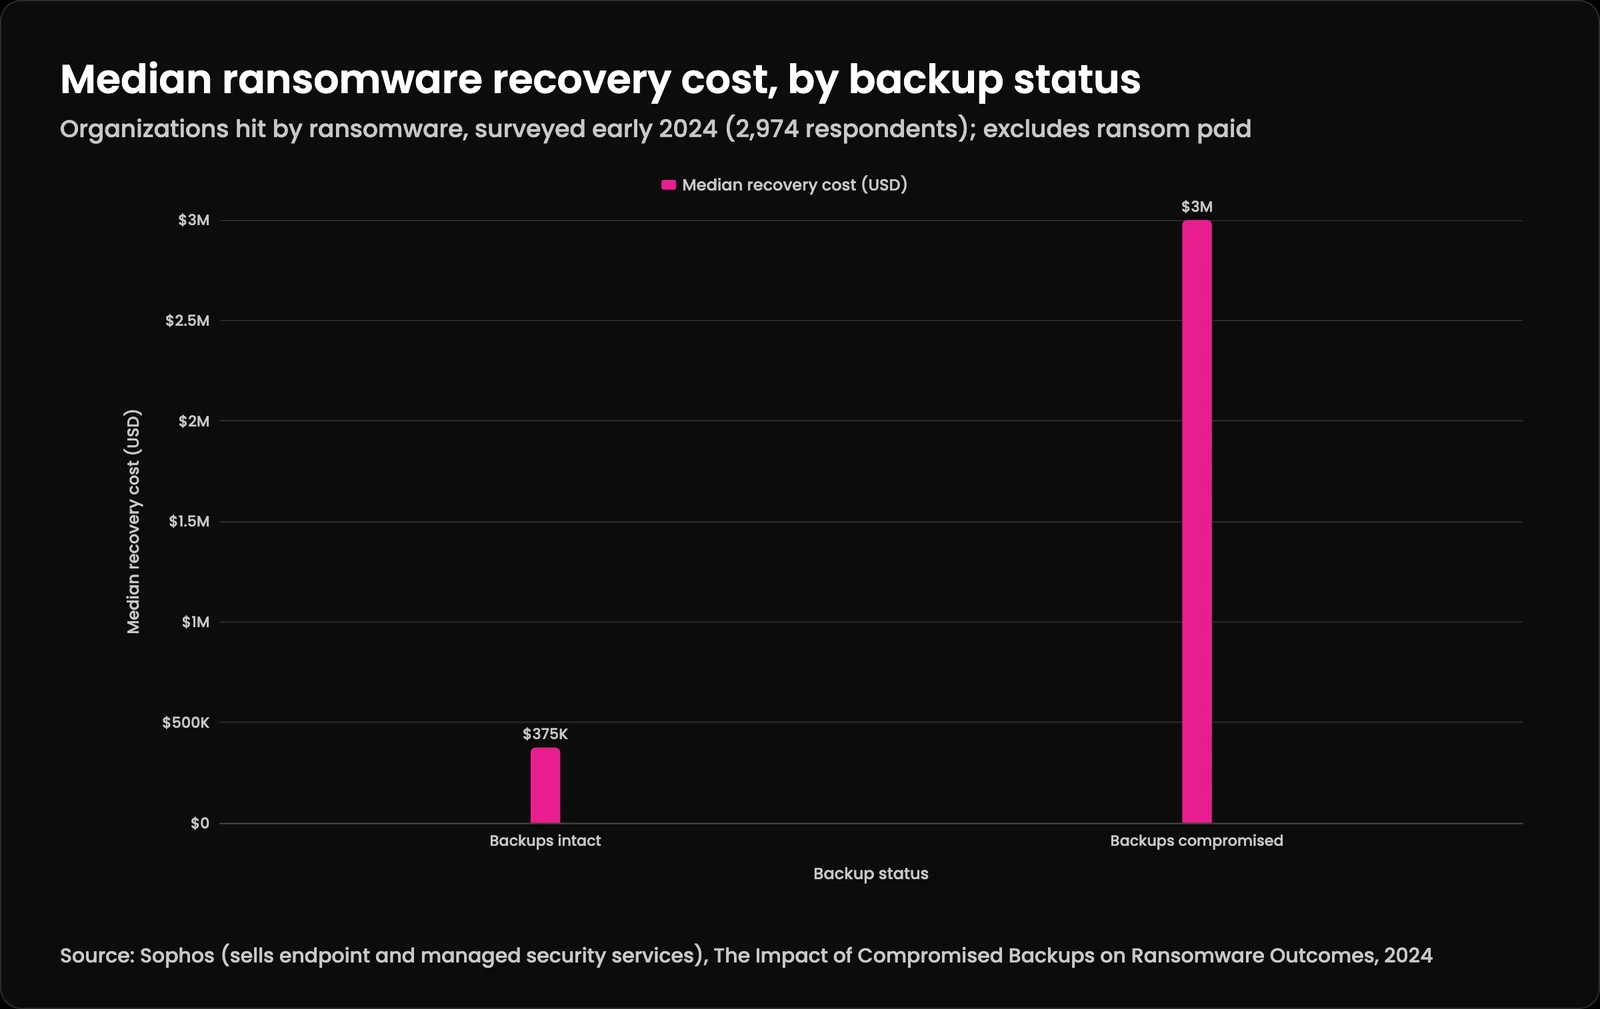
| Backup status | Median recovery cost (USD) |
|---|---|
| Backups intact | $375K |
| Backups compromised | $3M |
Those surveys cover organizations with 100 or more employees, so a five-person firm's bill will be smaller. For a small firm, the cost side of how to back up a business against ransomware is a drive, a storage bill and a few hours a quarter. The ratio is the useful part: a protected backup was the difference between a bad month and a very bad year. The Massachusetts side of the math, notification, legal review and lost clients, is covered in what a data breach costs a Massachusetts business.
If you have no backup system in place, start here:
The businesses that recover best from ransomware are usually the ones that never had to consider paying the ransom. What they had in common was a backup strategy that was set up correctly and tested regularly, nothing more exotic than that.
A basic 3-2-1 backup setup can cost under $200/year. A quality external drive runs $50-100, and cloud backup services like Backblaze or Wasabi list storage at about $7-8/month per terabyte (Backblaze B2 at $6.95 and Wasabi at $7.99, as of November 2026). Enterprise-grade immutable storage adds cost but is increasingly available at SMB price points. The math is simple: compare $200/year to the $1.7 million average recovery cost in Sophos's 2026 survey. The backup pays for itself if it prevents even a few hours of downtime over its lifetime.
No. Cloud platforms protect against their own infrastructure failures: hardware faults, data center outages. They do not protect against ransomware encrypting files via your synced account, accidental deletion, or a compromised admin account wiping data. Both Google and Microsoft operate on a "shared responsibility model" where data protection is explicitly your responsibility. You need a third-party backup that copies your cloud data to a separate, protected location.
Microsoft's own shared responsibility page lists customer data, configurations, and identities as the customer's job in every model, Microsoft 365 included. Brian Gagne's guide to Microsoft 365 and Google Workspace for small business covers how long each suite keeps deleted items and why neither suite counts as a backup.
An offsite backup is stored in a different physical location: a cloud server, a drive at a second office. An air-gapped backup goes further: it's disconnected from your network entirely except during active backup windows. A regular cloud backup syncing continuously can still be reached by ransomware through your sync agent's credentials. An air-gapped backup, whether a USB drive that's physically unplugged or cloud storage using write-only, time-locked immutable policies, can't be touched because there's no live connection to exploit.
It depends on data volume and your restore method. A local backup of a small business (under 500 GB) can restore in 1-4 hours. A cloud restore of the same data over a standard business internet connection might take 12-24 hours: 500 GB is 4,000 gigabits, so at 100 Mbps the download alone runs about 11 hours before anything is checked or reinstalled. Full system rebuilds, where you're reconfiguring servers and applications from scratch, not just restoring files, can take several business days even with good backups. This is exactly why testing restore times matters: you need to know whether your recovery timeline matches what your business can survive.
Yes, if the backup maintains a live connection to your network. Ransomware that compromises an account with access to cloud storage (through synced folders, API keys, or saved credentials) can encrypt or delete cloud backups just as easily as local files. This is why immutable storage and write-only backup credentials matter. With immutable storage, even a fully compromised account can't modify or delete existing backups during the retention window. It's one of the strongest protections available for backups.
Yes, and it's short. List what you'd need to reopen (files, databases, configurations, credentials, email). Automate backups to a local device and a cloud service. Make one copy offline or immutable, under an admin account nobody uses for daily work. Keep enough history to reach a point before an intrusion would have started. Restore from a random backup every quarter, time it, and write the result down. Keep your first-hour response steps (isolate, don't connect the backup, report) somewhere you can find them without the network.
Coalition put average global cyber claim severity at $116,000 for 2025, well under most policy limits. That means cyber insurance exclusions and sublimits, not the limit, decide what you collect.
Cyber resilience tools cost versus breach recovery and fines is a recurring number you choose against a one-time number you do not. IBM's 2026 average breach is $4.99 million globally and $11.5 million in the US. The fine is rarely the largest line.
A vendor exit plan shows regulators and your board you could leave a critical software vendor. Exits are rare: the UK CMA found about 0.1% of AWS, Microsoft and Google customers switched provider each year from 2020 to 2022. Four questions the plan answers, and a yearly test.
Work With Us
Kief Studio builds, protects, automates, and supports full-stack systems for businesses up to $50M ARR.
Newsletter
Strategy, psychology, AI adoption, and the patterns that actually compound. No spam, easy to leave.
Subscribe